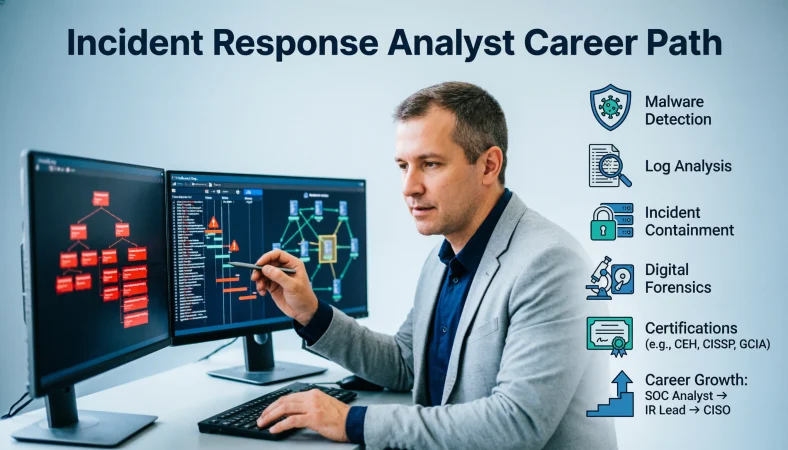
Incident response analyst jobs focus on identifying, investigating, and managing cybersecurity incidents such as malware infections, phishing attacks, and data breaches. These roles suit people who enjoy solving technical problems, analyzing suspicious activity, and helping organizations recover from cyber threats.
Top alternatives: Cybersecurity Incident Analyst Jobs, Security Operations Center Analyst Jobs, Cyber Incident Responder Jobs, Digital Forensics Analyst Jobs, Threat Detection Analyst Jobs
Incident response analyst jobs are a strong career option for people interested in cybersecurity, threat investigation, and digital defense. With the right technical skills, practical experience, and certifications, you can build a career protecting organizations from cyberattacks.
What Are Incident Response Analyst Jobs?
Investigating and Detecting Security Threats
1. Investigate Cybersecurity Incidents
Example: Use this responsibility when describing a role that investigates suspicious logins, malware alerts, or potential data breaches.
Meaning: You identify what happened during a security incident and help determine its cause.
2. Detect Suspicious Network Activity
Example: Include this duty when applying for positions that monitor network traffic for unusual patterns.
Meaning: You look for signs that attackers may be accessing or disrupting a network.
3. Analyze Security Alerts
Example: Use this when explaining how analysts review alerts from security monitoring systems.
Meaning: You determine whether an alert represents a genuine threat or a false positive.
Containing Threats and Supporting Recovery
4. Contain Active Threats
Example: Mention this responsibility when a job description includes isolating compromised devices.
Meaning: You help limit an attack’s impact before it spreads further.
5. Support Incident Recovery
Example: Use this when discussing the steps involved in restoring affected systems after an attack.
Meaning: You help organizations return to normal operations safely.
6. Preserve Digital Evidence
Example: Include this duty when applying for roles involving forensic investigations.
Meaning: You protect relevant evidence so investigators can examine what happened.
Analyzing Evidence and Documenting Findings
7. Review Security Logs
Example: Use this when describing experience analyzing authentication records and endpoint logs.
Meaning: You examine system activity to identify suspicious behavior.
8. Document Security Incidents
Example: Mention this when explaining how you prepare incident timelines and investigation reports.
Meaning: You create clear records of the incident, response actions, and findings.
9. Identify Attack Techniques
Example: Use this for roles that investigate phishing, credential theft, or ransomware activity.
Meaning: You determine how attackers gained access and what methods they used.
Collaborating and Improving Security
10. Collaborate With Security Teams
Example: Include this when describing teamwork with SOC analysts, threat hunters, and IT administrators.
Meaning: You coordinate with other specialists to investigate and resolve threats.
11. Recommend Security Improvements
Example: Use this when explaining how you suggest stronger access controls after an incident.
Meaning: You help prevent similar security problems from happening again.
12. Monitor Emerging Threats
Example: Mention this responsibility when applying to teams that track new attack methods.
Meaning: You stay aware of evolving threats that could affect your organization.
Incident Response Analyst Jobs for Beginners
Building Essential Cybersecurity Skills
1. Start With Security Fundamentals
Example: Use this goal when planning your first steps into cybersecurity without previous industry experience.
Meaning: You build a foundation in networks, operating systems, and basic security concepts.
2. Learn How Networks Work
Example: Include this in a beginner learning plan focused on IP addresses, DNS, ports, and network traffic.
Meaning: You develop the knowledge needed to understand suspicious communications.
3. Practice Reading Security Logs
Example: Use this activity when building a home lab with sample authentication and system logs.
Meaning: You learn how to spot unusual events in technical records.
Gaining Hands-On Experience
4. Explore Entry-Level SOC Roles
Example: Consider this route when searching for your first full-time cybersecurity position.
Meaning: A Security Operations Center role can provide relevant monitoring and investigation experience.
5. Build a Cybersecurity Home Lab
Example: Mention this project when demonstrating practical learning on your resume.
Meaning: You gain hands-on experience in a controlled environment.
6. Study Basic Incident Handling
Example: Use this goal when learning how teams prepare for, detect, contain, and recover from incidents.
Meaning: You understand the typical stages of incident response.
Developing Technical Skills and a Portfolio
7. Learn a Scripting Language
Example: Practice Python by writing a script that extracts suspicious IP addresses from sample logs.
Meaning: You develop automation skills that can make investigations more efficient.
8. Understand Windows and Linux
Example: Include both systems in a beginner lab to practice reviewing logs and processes.
Meaning: You learn how to investigate activity across common operating systems.
9. Create a Small Portfolio
Example: Publish sanitized lab reports that explain your investigation steps and findings.
Meaning: You give employers evidence of your practical skills without needing previous job experience.
Preparing for Job Applications and Growth
10. Apply for Junior Security Positions
Example: Search for junior SOC analyst, security analyst, and incident response trainee openings.
Meaning: You target roles that may provide a pathway into incident response.
11. Practice Technical Interviews
Example: Prepare to explain how you would investigate a suspicious login or phishing alert.
Meaning: You improve your ability to communicate your technical reasoning.
12. Keep Learning Consistently
Example: Set aside time each week to study new threats and complete practical exercises.
Meaning: You gradually strengthen your knowledge and confidence.
Entry-Level Incident Response Analyst Jobs Without Experience
Starting With Junior Security and Training Roles
1. Junior SOC Analyst
Example: Target this position when you have foundational security knowledge but limited professional experience.
Meaning: You monitor alerts and help identify potential security incidents.
2. Security Operations Intern
Example: Apply for internships that provide exposure to security monitoring and incident documentation.
Meaning: You gain supervised experience in a professional security environment.
3. Cybersecurity Trainee
Example: Consider structured trainee programs that teach security tools and investigation procedures.
Meaning: You learn job-specific skills while preparing for more advanced responsibilities.
Building Experience Through IT and Security Support
4. IT Support Technician With Security Duties
Example: Look for IT support positions that involve account security, endpoint protection, and access troubleshooting.
Meaning: You build transferable experience that can support a later move into cybersecurity.
5. Security Monitoring Analyst
Example: Search for junior roles that involve reviewing alerts and escalating suspicious events.
Meaning: You gain experience recognizing threats and following response procedures.
6. Vulnerability Management Assistant
Example: Apply for roles that help track software vulnerabilities and coordinate remediation.
Meaning: You learn how security weaknesses are identified and prioritized.
Exploring Practical Investigation and Monitoring Roles
7. Digital Forensics Intern
Example: Consider internships involving evidence handling and basic forensic analysis.
Meaning: You gain exposure to investigations that may overlap with incident response.
8. Cybersecurity Apprenticeship
Example: Search for paid apprenticeships combining practical security work with structured training.
Meaning: You develop experience while learning from experienced professionals.
9. Managed Security Services Analyst
Example: Explore junior openings at providers that monitor security events for multiple clients.
Meaning: You may gain experience with different environments and incident types.
Preparing for Direct Incident Response Work
10. Threat Monitoring Trainee
Example: Apply for positions that focus on identifying suspicious activity using established playbooks.
Meaning: You build foundational threat detection and escalation skills.
11. IT Security Assistant
Example: Look for support roles involving endpoint security, access reviews, and incident tickets.
Meaning: You gain exposure to security operations and organizational procedures.
12. Junior Cyber Incident Analyst
Example: Apply when a listing emphasizes investigation support, documentation, and supervised response tasks.
Meaning: You work toward a role focused directly on incident handling.
Technical Skills for Incident Response Analyst Jobs
Network Monitoring and Security Event Analysis
1. Network Analysis
Example: Demonstrate your understanding of DNS queries, IP traffic, and suspicious connections in a lab report.
Meaning: You learn to investigate how devices communicate and where malicious activity may occur.
2. Log Analysis
Example: Practice connecting authentication events with endpoint and network logs.
Meaning: You reconstruct activity by examining recorded events.
3. SIEM Platforms
Example: Build sample searches in a security information and event management platform.
Meaning: You learn how to correlate security events and investigate alerts.
Endpoint Protection and Operating System Skills
4. Endpoint Detection and Response
Example: Study how endpoint tools detect suspicious processes and isolate affected devices.
Meaning: You understand how organizations investigate threats on computers and servers.
5. Operating System Knowledge
Example: Practice reviewing Windows event logs and Linux authentication records.
Meaning: You learn where important system activity is recorded.
6. Python Scripting
Example: Write a simple script that sorts sample indicators of compromise into a readable report.
Meaning: You automate repetitive tasks and organize investigation data.
Forensics, Malware, and Cloud Security
7. Digital Forensics Basics
Example: Learn how to preserve sample evidence and document its handling in a controlled lab.
Meaning: You understand how to examine digital artifacts without compromising evidence integrity.
8. Malware Analysis Fundamentals
Example: Study safe, isolated malware-analysis exercises using trusted training materials.
Meaning: You learn to recognize malicious behavior and understand potential impact.
9. Cloud Security Knowledge
Example: Practice investigating suspicious sign-ins and configuration changes in a cloud lab.
Meaning: You prepare to investigate incidents involving cloud services and accounts.
Identity Security, Threat Intelligence, and Reporting
10. Identity and Access Management
Example: Learn how multi-factor authentication, privileged accounts, and access logs affect investigations.
Meaning: You understand common identity-related attack paths.
11. Threat Intelligence
Example: Practice researching sample indicators using reputable threat intelligence sources.
Meaning: You add context that helps determine whether an event is connected to a known threat.
12. Incident Documentation
Example: Prepare a mock report with a timeline, impact assessment, evidence, and recommended actions.
Meaning: You communicate investigation results clearly and consistently.
Certifications for Incident Response Analyst Jobs
Foundational Cybersecurity Certifications
1. CompTIA Security+
Example: Consider this certification when building broad foundational cybersecurity knowledge.
Meaning: It can help demonstrate understanding of security concepts, risks, and controls.
2. CompTIA CySA+
Example: Explore this option when preparing for roles involving security monitoring and threat analysis.
Meaning: It focuses on practical defensive security and analytical skills.
3. GIAC Certified Incident Handler
Example: Consider this specialist certification if your career goals center on incident handling and response.
Meaning: It validates knowledge relevant to managing and investigating security incidents.
Advanced Security and Incident Handling Credentials
4. Certified Incident Handler
Example: Review incident-handling certifications that match your experience level and target employers.
Meaning: Relevant credentials can demonstrate structured knowledge of response procedures.
5. Certified Information Systems Security Professional
Example: Consider CISSP later in your career if you meet its experience requirements.
Meaning: It covers broad security management and technical concepts beyond entry-level incident response.
6. Certified Ethical Hacker
Example: Explore ethical hacking training to better understand attacker methods and techniques.
Meaning: Offensive security knowledge can help you recognize and investigate attack behavior.
Forensics and Platform-Specific Certifications
7. GIAC Certified Forensic Analyst
Example: Research this option if you want to specialize in forensic investigations and evidence analysis.
Meaning: It supports deeper study of digital forensic techniques.
8. Microsoft Security Certifications
Example: Review current Microsoft security credentials that align with your target security platform.
Meaning: Platform-specific training can help if employers use Microsoft’s security ecosystem.
9. Cloud Security Certifications
Example: Choose a relevant cloud security credential if your target roles involve cloud incidents.
Meaning: You develop knowledge of cloud threats, controls, and investigations.
Practical Tools and Defensive Security Training
10. Splunk Training and Certifications
Example: Study Splunk searches and dashboards if job listings frequently mention the platform.
Meaning: You strengthen your ability to examine security data in that environment.
11. Security Blue Team Training
Example: Explore defensive security courses with practical investigation exercises.
Meaning: You can develop hands-on skills in detection, triage, and incident handling.
12. Vendor-Specific EDR Training
Example: Complete training for the endpoint security platform used by your target employers.
Meaning: You gain familiarity with tools that may appear in real incident response workflows.
Incident Response Analyst Jobs Salary and Pay Expectations
Understanding Salary Levels and Contract Rates
1. Entry-Level Salary Research
Example: Compare junior cybersecurity salaries in the city or country where you plan to work.
Meaning: You establish a realistic starting point based on your local market.
2. Mid-Level Analyst Pay
Example: Review salary ranges for roles requiring independent investigations and incident coordination.
Meaning: Experience and greater responsibility can influence earning potential.
3. Senior Analyst Compensation
Example: Compare senior incident response positions that lead complex investigations.
Meaning: Advanced expertise may qualify you for higher compensation.
Comparing Employment Types and Specialized Roles
4. Contract Incident Response Rates
Example: Review contract listings that specify hourly or daily rates for incident response work.
Meaning: Contract compensation may differ from permanent employee salaries.
5. Government Cybersecurity Salaries
Example: Check official public-sector salary scales when applying for government security roles.
Meaning: Government pay may follow structured grades or experience-based bands.
6. Remote Job Compensation
Example: Compare remote openings that hire locally with those offering location-adjusted salaries.
Meaning: Remote work does not always mean the same pay across different regions.
Evaluating Specializations and Industry Differences
7. Cloud Incident Response Pay
Example: Research salaries for roles involving cloud investigations and identity security.
Meaning: Specialized cloud knowledge may affect compensation.
8. Digital Forensics Salary Comparison
Example: Compare forensic analyst and incident response listings to understand overlapping career paths.
Meaning: Related roles may have different responsibilities and pay ranges.
9. Certification and Salary
Example: Compare job listings to see whether employers reward particular credentials.
Meaning: Certifications may help with eligibility, but they do not guarantee a raise.
Assessing Benefits and Negotiating Your Pay
10. Industry-Based Pay Differences
Example: Compare cybersecurity positions in finance, healthcare, consulting, and technology.
Meaning: Industry, risk exposure, and organizational size can affect compensation.
11. Benefits and Total Compensation
Example: Review health benefits, bonuses, retirement plans, training budgets, and on-call allowances.
Meaning: Your total employment package can be worth more than base salary alone.
12. Salary Negotiation Preparation
Example: Use current market data and documented achievements to support a reasonable salary request.
Meaning: Evidence helps you negotiate with confidence.
Remote Incident Response Analyst Jobs
Finding Remote Opportunities and Checking Requirements
1. Search Remote-First Employers
Example: Prioritize companies that explicitly advertise remote cybersecurity operations.
Meaning: You focus on employers with established remote-work arrangements.
2. Check Geographic Restrictions
Example: Read each listing for country, state, residency, or time-zone requirements.
Meaning: Some remote positions are available only in specific locations.
3. Explore Managed Security Providers
Example: Look for remote security monitoring and incident response positions at managed security providers.
Meaning: These employers may offer distributed teams and structured investigation workflows.
Building Skills for Remote Security Work
4. Build Strong Written Communication
Example: Practice writing concise incident updates for teammates in different time zones.
Meaning: Clear documentation helps remote teams coordinate effectively.
5. Learn Secure Remote Work Practices
Example: Study secure access, device management, and confidential evidence handling.
Meaning: You protect sensitive information while working outside the office.
6. Prepare for On-Call Duties
Example: Check whether the listing includes overnight shifts or an incident escalation rotation.
Meaning: Some remote response roles still require availability outside standard hours.
Demonstrating Your Readiness for Remote Roles
7. Demonstrate Independent Problem-Solving
Example: Include a portfolio project showing how you investigated an alert from start to finish.
Meaning: You show that you can work methodically with limited supervision.
8. Practice Virtual Interviews
Example: Prepare to explain a sample investigation clearly during a video interview.
Meaning: You demonstrate technical knowledge and communication skills remotely.
9. Check Equipment Requirements
Example: Review whether the employer provides a secure workstation or expects specific equipment.
Meaning: You understand the practical requirements before accepting an offer.
Evaluating Policies and Strengthening Applications
10. Review Data Handling Policies
Example: Ask how the team securely accesses and stores incident evidence.
Meaning: You show awareness of confidentiality and evidence protection.
11. Compare Remote and Hybrid Roles
Example: Include hybrid openings if fully remote positions are limited in your area.
Meaning: You expand your options without losing sight of your preferred work setup.
12. Tailor Your Resume for Remote Work
Example: Highlight documented investigations, independent projects, and remote collaboration experience.
Meaning: You show employers that you can contribute effectively to a distributed team.
Incident Response Analyst Jobs for Experienced Professionals
Senior Investigation and Team Leadership Roles
1. Senior Incident Response Analyst
Example: Target positions requiring ownership of complex investigations and incident coordination.
Meaning: You take responsibility for deeper analysis and response decisions.
2. Incident Response Team Lead
Example: Apply for roles that involve assigning investigations and coordinating response activities.
Meaning: You guide analysts and help keep incident handling organized.
3. Digital Forensics Specialist
Example: Explore positions focused on examining devices, artifacts, and evidence after security incidents.
Meaning: You specialize in understanding what happened through forensic analysis.
Advanced Threat Detection and Specialized Response
4. Threat Hunter
Example: Look for roles that proactively search security data for hidden attacker activity.
Meaning: You investigate suspicious behavior that automated alerts may not identify.
5. Cloud Incident Responder
Example: Target jobs involving cloud identity, workloads, audit logs, and configuration changes.
Meaning: You specialize in investigating threats within cloud environments.
6. Malware Incident Specialist
Example: Apply for roles that analyze malicious files and investigate malware outbreaks.
Meaning: You focus on understanding malware behavior and limiting its impact.
Consulting and Security Engineering Opportunities
7. Ransomware Response Analyst
Example: Consider roles involving containment, evidence collection, and recovery coordination during ransomware incidents.
Meaning: You help organizations respond to disruptive extortion attacks.
8. Incident Response Consultant
Example: Explore consulting roles that investigate incidents for different clients.
Meaning: You apply your expertise across varied environments and security challenges.
9. Detection Engineer
Example: Look for positions that develop and refine detection rules based on investigation findings.
Meaning: You help security teams identify threats more accurately.
Strategic Incident Management and Architecture
10. Security Incident Manager
Example: Target roles coordinating technical responders, business stakeholders, and recovery teams.
Meaning: You help manage the broader operational response to security incidents.
11. Threat Intelligence Analyst
Example: Consider positions that connect investigation findings with broader attacker behavior.
Meaning: You turn threat information into useful security context.
12. Incident Response Architect
Example: Explore advanced roles designing response processes, playbooks, and security workflows.
Meaning: You help build the systems and procedures that support effective incident response.
Professional Skills Employers Want in Incident Response Analysts
Critical Thinking and Analytical Skills
1. Critical Thinking
Example: Demonstrate how you compare multiple explanations before deciding whether an alert is malicious.
Meaning: You evaluate evidence instead of jumping to conclusions.
2. Attention to Detail
Example: Explain how you verify timestamps, account names, and system identifiers in an investigation.
Meaning: You reduce the risk of overlooking important evidence.
3. Clear Communication
Example: Practice explaining a technical incident in plain language for a nontechnical manager.
Meaning: You make security findings understandable to different audiences.
Teamwork and Decision-Making Skills
4. Team Collaboration
Example: Describe a project where you coordinated tasks and shared findings with others.
Meaning: You show that you can contribute to a coordinated response.
5. Calm Decision-Making
Example: Explain how you would follow an approved playbook during a high-pressure incident.
Meaning: You stay methodical when quick decisions matter.
6. Time Management
Example: Describe how you prioritize urgent security alerts over routine administrative tasks.
Meaning: You focus effort on the incidents with the greatest potential impact.
Adaptability and Professional Judgment
7. Adaptability
Example: Discuss how you learn a new security platform or investigation procedure.
Meaning: You can adjust as threats and technologies change.
8. Ethical Judgment
Example: Explain how you protect confidential evidence and follow approved access procedures.
Meaning: You handle sensitive information responsibly.
9. Curiosity
Example: Show how you investigate the root cause of an alert rather than stopping at the first explanation.
Meaning: You want to understand the full picture.
Documentation, Accountability, and Growth
10. Accurate Documentation
Example: Present a clear timeline of actions and evidence from a lab investigation.
Meaning: You make your findings easier for teammates to verify and use.
11. Accountability
Example: Describe how you report an error, correct the record, and communicate the change.
Meaning: You take responsibility for the quality of your work.
12. Continuous Learning
Example: Share a recent lab, course, or technical exercise that expanded your knowledge.
Meaning: You demonstrate a commitment to improving your skills.
Best Places to Find Incident Response Analyst Jobs
1. LinkedIn Jobs
Example: Search for incident response analyst openings and filter by experience level or work arrangement.
Meaning: You can explore employer listings and professional networking opportunities.
2. Indeed
Example: Compare incident response listings with related cybersecurity analyst roles.
Meaning: You broaden your search across employers and job categories.
3. Glassdoor
Example: Review relevant job openings alongside available company and salary information.
Meaning: You can research potential employers as well as positions.
4. Company Career Pages
Example: Check the official careers pages of cybersecurity companies and large organizations.
Meaning: You may find direct employer listings and role requirements.
5. Government Career Portals
Example: Review official government vacancies if you are interested in public-sector cybersecurity.
Meaning: You can identify roles with formal eligibility and application requirements.
6. Cybersecurity Company Websites
Example: Explore career pages for incident response consultancies and managed security providers.
Meaning: You focus on organizations that offer security investigation services.
7. Remote Job Boards
Example: Filter for remote cybersecurity jobs and verify the location requirements for each role.
Meaning: You identify opportunities that fit your preferred work arrangement.
8. University Career Services
Example: Use career services if you are studying computer science or cybersecurity.
Meaning: You may find internships, entry-level openings, and employer events.
9. Cybersecurity Communities
Example: Follow reputable professional communities that share vacancies and career advice.
Meaning: You can discover openings and learn about industry expectations.
10. Recruitment Agencies
Example: Contact recruiters who specialize in cybersecurity and digital forensics.
Meaning: They may help match your experience with relevant vacancies.
11. Professional Conferences
Example: Attend cybersecurity events where employers discuss teams, openings, and required skills.
Meaning: You can build connections while learning about the field.
12. Alumni Networks
Example: Ask former classmates or graduates about entry-level security opportunities.
Meaning: Professional connections may help you discover suitable positions.
How to Write a Resume for Incident Response Analyst Jobs
Target Your Resume to the Job
1. Use a Targeted Resume Headline
Example: Write a headline such as “Junior Cybersecurity Analyst | Incident Investigation and Log Analysis.”
Meaning: You quickly communicate your career focus to recruiters.
2. Match Relevant Job Requirements
Example: Highlight log analysis when the vacancy specifically requests investigation experience.
Meaning: You make your most relevant qualifications easier to identify.
3. List Technical Skills Clearly
Example: Group skills under networking, SIEM, endpoint security, scripting, and operating systems.
Meaning: You help employers scan your technical background efficiently.
Showcase Practical Experience and Results
4. Highlight Hands-On Projects
Example: Describe a lab where you investigated suspicious authentication events and documented findings.
Meaning: You demonstrate practical knowledge, even if you are new to the industry.
5. Use Measurable Achievements
Example: Explain how a script reduced the manual steps in a sample log-review task.
Meaning: You show the outcome of your work instead of listing duties alone.
6. Include Relevant Certifications
Example: List completed certifications and accurately label any training still in progress.
Meaning: You give employers a clear view of your professional development.
Demonstrate Investigation Skills and Credibility
7. Describe Investigation Methods
Example: Mention how you correlated logs, created timelines, or documented indicators in a lab.
Meaning: You show how you approach security problems.
8. Keep Formatting Readable
Example: Use clear headings, consistent dates, and concise bullet points.
Meaning: You make your resume easier to review.
9. Avoid Unsupported Claims
Example: Describe a simulated ransomware investigation as a lab exercise rather than a real breach.
Meaning: You maintain credibility and accurately represent your experience.
Polish Your Resume Before Applying
10. Add Relevant Tools
Example: Name the security platforms you have genuinely used and explain your level of experience.
Meaning: You help recruiters assess your technical familiarity.
11. Include Communication Skills
Example: Mention incident reports, team presentations, or documented project findings.
Meaning: You show that you can explain technical work.
12. Proofread Before Applying
Example: Check technical terms, dates, contact details, and spelling before submitting your application.
Meaning: You present a polished and professional application.
Incident Response Analyst Job Interview Questions
Incident Response Fundamentals
1. What Is Incident Response?
Example: Prepare a concise explanation covering identification, containment, investigation, eradication, and recovery.
Meaning: You demonstrate a basic understanding of the incident response lifecycle.
2. How Would You Investigate a Phishing Email?
Example: Practice describing how you inspect the message, examine links, and check related security logs.
Meaning: You show a structured approach to a common security incident.
3. What Would You Do After Detecting Malware?
Example: Explain how you would follow organizational procedures to validate the alert and contain affected systems.
Meaning: You demonstrate that you understand safe and coordinated response.
Security Monitoring and Alert Analysis
4. How Do You Prioritize Security Alerts?
Example: Describe how you assess severity, scope, asset importance, and evidence of active compromise.
Meaning: You show that you can prioritize based on risk.
5. What Is a SIEM?
Example: Explain how a SIEM collects and correlates security data from multiple sources.
Meaning: You show familiarity with a core security monitoring technology.
6. What Is an Indicator of Compromise?
Example: Give examples such as a suspicious file hash, malicious IP address, or unusual domain.
Meaning: You demonstrate knowledge of evidence that may indicate malicious activity.
Incident Handling and Documentation
7. How Would You Handle a Data Breach?
Example: Explain how you would follow the incident response plan, preserve evidence, and escalate appropriately.
Meaning: You show awareness of coordinated response and reporting requirements.
8. How Do You Distinguish a False Positive?
Example: Describe how you validate an alert by checking supporting logs and contextual evidence.
Meaning: You show analytical thinking instead of relying on alerts alone.
9. How Do You Document an Incident?
Example: Outline a report containing the timeline, affected assets, evidence, actions, and recommendations.
Meaning: You demonstrate clear and repeatable reporting.
Technical Knowledge and Career Motivation
10. What Is the Difference Between Containment and Eradication?
Example: Explain that containment limits the spread while eradication removes the threat from affected systems.
Meaning: You understand two distinct response objectives.
11. How Do You Stay Updated on Cyber Threats?
Example: Discuss reputable threat reports, security advisories, technical labs, and professional training.
Meaning: You show a practical commitment to continuous learning.
12. Why Do You Want This Role?
Example: Connect your interest in investigations with the organization’s security mission and the role’s requirements.
Meaning: You explain your motivation in a specific and credible way.
Career Growth and Advancement in Incident Response Analyst Jobs
1. Move From Junior to Mid-Level Analyst
Example: Build a record of accurate investigations, strong documentation, and dependable incident handling.
Meaning: You demonstrate readiness for greater responsibility.
2. Specialize in Digital Forensics
Example: Develop deeper skills in evidence preservation and artifact analysis.
Meaning: You create a pathway toward forensic investigation work.
3. Explore Threat Hunting
Example: Practice proactive searches for suspicious behavior across security datasets.
Meaning: You move beyond alert-driven investigations.
4. Develop Cloud Security Expertise
Example: Study identity events, cloud audit logs, and workload security.
Meaning: You prepare for incidents involving cloud infrastructure.
5. Learn Detection Engineering
Example: Create and test detection rules using realistic lab data.
Meaning: You help improve how security teams identify threats.
6. Lead Incident Investigations
Example: Volunteer to coordinate a simulated incident exercise and document the response.
Meaning: You develop leadership and investigation management skills.
7. Improve Automation Skills
Example: Write scripts that organize indicators or enrich sample alerts with context.
Meaning: You reduce repetitive work and improve consistency.
8. Build Industry Connections
Example: Join professional cybersecurity groups and exchange knowledge with experienced analysts.
Meaning: You expand your professional network and learn from peers.
9. Develop Executive Communication
Example: Practice summarizing an incident’s impact and response plan for leadership.
Meaning: You become better at communicating risk and business impact.
10. Learn Incident Response Frameworks
Example: Study recognized guidance, such as NIST incident response recommendations.
Meaning: You understand structured approaches to preparing for and managing incidents.
11. Consider Consulting
Example: Build experience in client communication, reporting, and varied investigation environments.
Meaning: You may qualify for roles supporting multiple organizations.
12. Plan Your Next Career Step
Example: Compare your current skills with the requirements of senior analyst or specialist vacancies.
Meaning: You can target learning that supports your long-term goals.
Incident Response Analyst Jobs: Common Mistakes to Avoid
Application and Resume Mistakes
1. Applying Without Reading Requirements
Example: Check the required skills, experience, location, and clearance conditions before applying.
Meaning: You avoid wasting time on unsuitable vacancies.
2. Ignoring Hands-On Practice
Example: Pair certification study with practical log analysis and investigation exercises.
Meaning: You build skills you can demonstrate during interviews.
3. Overloading Your Resume With Keywords
Example: Include tools and technologies you have actually used rather than listing every security product.
Meaning: You keep your resume credible and relevant.
Unrealistic Expectations and Role Confusion
4. Expecting One Certification to Guarantee a Job
Example: Combine certification study with a portfolio and targeted applications.
Meaning: You recognize that hiring decisions depend on several factors.
5. Confusing Security Roles
Example: Compare incident response duties with penetration testing, governance, and general IT support.
Meaning: You apply for jobs that align with your preferred work.
6. Neglecting Communication Skills
Example: Practice writing a brief incident summary for a nontechnical audience.
Meaning: You improve a skill that matters during real investigations.
Professionalism and Workplace Requirements
7. Misrepresenting Lab Experience
Example: Clearly label simulated incidents as projects rather than professional client work.
Meaning: You protect your credibility with employers.
8. Ignoring Shift Requirements
Example: Check whether a role involves overnight coverage, weekend shifts, or on-call rotations.
Meaning: You understand the working conditions before accepting an offer.
9. Forgetting to Follow Up
Example: Send a brief, professional follow-up when appropriate after an interview.
Meaning: You show interest without pressuring the hiring team.
Eligibility, Interview Preparation, and Growth
10. Overlooking Local Eligibility Rules
Example: Verify work authorization, residency, and background-check requirements where applicable.
Meaning: You confirm that you can legally and practically take the position.
11. Skipping Interview Practice
Example: Rehearse a structured response to a sample phishing or malware alert.
Meaning: You communicate your reasoning more clearly under pressure.
12. Stopping Your Learning
Example: Continue practicing with updated scenarios and reviewing new security guidance.
Meaning: You keep your skills relevant as attack methods evolve.
FAQs
What do incident response analysts do?
They investigate security incidents, help contain threats, preserve evidence, and support recovery.
Are incident response analyst jobs good for beginners?
Yes. Junior SOC roles, internships, and security trainee positions can provide useful starting experience.
Do incident response analysts need a degree?
Not always. Requirements vary, and practical skills, experience, and certifications may also matter.
Can I get an incident response analyst job without experience?
It is possible, especially through entry-level security roles, internships, apprenticeships, and hands-on projects.
What skills are most important for incident response analysts?
Log analysis, networking, security monitoring, incident handling, documentation, and clear communication are valuable.
How much do incident response analysts earn?
Pay varies by location, experience, industry, and specialization. Check current local job listings for realistic ranges.
Are incident response analyst jobs available remotely?
Yes, some are remote or hybrid, but employers may impose location, shift, or on-call requirements.
Which certifications are useful for incident response analyst jobs?
Security+, CySA+, and specialized incident handling or forensic credentials may be relevant, depending on your goals.
Is incident response the same as a SOC analyst job?
They overlap, but SOC analysts often monitor alerts while incident responders focus more deeply on investigation and containment.
Do incident response analysts need coding skills?
Advanced coding is not always required, but basic Python or scripting can help automate repetitive tasks.
Is incident response a stressful career?
It can be demanding during major incidents, so communication, teamwork, and calm decision-making are important.
How can I prepare for an incident response analyst interview?
Review security fundamentals, practice incident scenarios, and prepare examples of your technical projects.
Conclusion
Incident response analyst jobs offer a practical path for people who want to investigate cyber threats, solve technical problems, and help organizations protect valuable systems and data. Whether you are starting with a home lab or moving up from a SOC position, focus on building real skills, documenting your projects, and learning how investigations work from detection through recovery.
Certifications can strengthen your profile, but hands-on practice and clear communication matter too. Start with roles that match your current experience, then grow toward specialized or senior positions as your knowledge improves. Save this guide for your next job search, share it with a cybersecurity beginner, and take your next career step with confidence.

1 thought on “150+ Incident Response Analyst Jobs: Skills, Duties, Salaries And Career Tips For 2026”