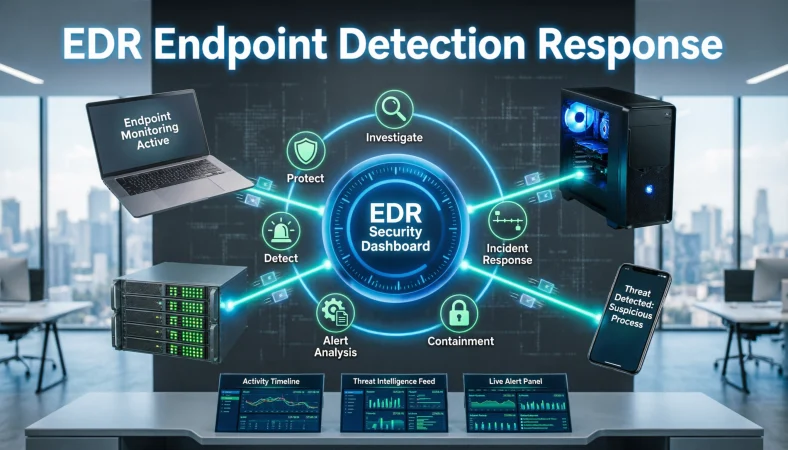
EDR endpoint detection response refers to security technology that continuously monitors endpoints, detects suspicious activity, investigates potential threats, and supports rapid response. It helps security teams understand what happened on devices and take action before an incident grows.
Top alternatives: endpoint detection and response, EDR security, endpoint threat detection, endpoint monitoring and response, endpoint cybersecurity
Ever wondered how security teams spot suspicious activity on laptops, servers, and other devices before a small incident turns into a much bigger headache? That is where EDR endpoint detection response enters the chat. Modern organizations have endpoints everywhere, and attackers can use a single compromised device as a starting point for a larger intrusion.
EDR solutions continuously collect endpoint activity, identify suspicious behavior, investigate alerts, and help security teams respond. You may encounter the term in cybersecurity reports, IT meetings, vendor comparisons, security job descriptions, or technical discussions.
Understanding the phrase makes it easier to compare security approaches and explain why endpoint visibility matters. From threat detection and investigation to containment and incident response, EDR connects multiple parts of endpoint security into one workflow.
EDR Endpoint Detection Response Basics
“EDR watches endpoints for suspicious activity.”
Example: Use this when explaining EDR to someone new to cybersecurity.
Meaning: It describes the basic monitoring function of EDR.
“Think of EDR as endpoint security with a memory.”
Example: Use this when explaining why historical endpoint data matters.
Meaning: It highlights the investigation value of recorded activity.
“EDR combines detection, investigation, and response.”
Example: Use this in an introductory cybersecurity presentation.
Meaning: It summarizes the three core activities associated with EDR.
“Endpoints become data sources for security teams.”
Example: Use this when discussing endpoint visibility.
Meaning: It explains how device activity can support investigations.
“EDR looks for behavior, not just known threats.”
Example: Use this when discussing behavioral detection.
Meaning: It highlights the importance of identifying suspicious patterns.
“Detection is only the beginning.”
Example: Use this when explaining why response capabilities matter.
Meaning: It emphasizes that finding a threat is not enough.
“EDR helps connect the dots.”
Example: Use this when explaining how security analysts investigate incidents.
Meaning: It describes how endpoint events can provide context.
“Endpoint visibility can reveal the bigger picture.”
Example: Use this when discussing incident investigation.
Meaning: It shows why endpoint telemetry can be valuable.
“EDR turns endpoint activity into security evidence.”
Example: Use this when discussing forensic investigation.
Meaning: It describes the investigative value of endpoint data.
“Monitor, detect, investigate, respond.”
Example: Use this as a simple summary of the EDR workflow.
Meaning: It presents the main stages in a memorable sequence.
“EDR is built around endpoint visibility.”
Example: Use this when explaining the foundation of endpoint detection.
Meaning: It identifies visibility as a central concept.
“Better endpoint context can support faster investigations.”
Example: Use this when discussing security operations efficiency.
Meaning: It connects visibility with investigation workflows.
Funny EDR Endpoint Detection Response Explanations
“Your laptop just got a security babysitter.”
Example: Use this in a beginner-friendly cybersecurity presentation.
Meaning: It humorously describes continuous endpoint monitoring.
“EDR notices when your endpoint starts acting suspicious.”
Example: Use this when introducing behavioral monitoring to beginners.
Meaning: It makes threat detection easier to understand.
“Cybersecurity, but with receipts.”
Example: Use this when explaining endpoint activity records.
Meaning: It highlights the value of historical evidence.
“Your endpoint has entered detective mode.”
Example: Use this when describing endpoint investigation capabilities.
Meaning: It gives a playful explanation of threat analysis.
“Someone gave the SOC a magnifying glass.”
Example: Use this when explaining security analyst visibility.
Meaning: It humorously represents detailed endpoint investigation.
“EDR says, ‘Interesting behavior. Let’s investigate.’”
Example: Use this when explaining behavioral alerts.
Meaning: It illustrates how suspicious activity can trigger investigation.
“The endpoint is talking, and EDR is taking notes.”
Example: Use this when describing telemetry collection.
Meaning: It explains how endpoint activity becomes security data.
“No endpoint gets to be mysterious anymore.”
Example: Use this when discussing improved endpoint visibility.
Meaning: It humorously emphasizes monitoring.
“Suspicious process? EDR has entered the chat.”
Example: Use this in a cybersecurity social post.
Meaning: It gives a casual explanation of detection capabilities.
“The SOC wants the whole story, not just the headline.”
Example: Use this when discussing incident context.
Meaning: It explains why detailed endpoint telemetry matters.
“EDR keeps the security receipts.”
Example: Use this when describing historical activity records.
Meaning: It presents endpoint telemetry as useful evidence.
“Attackers hate a device that tells on itself.”
Example: Use this in an awareness presentation about endpoint visibility.
Meaning: It humorously describes why endpoint monitoring can help defenders.
Professional EDR Endpoint Detection Response Examples
“EDR provides continuous endpoint monitoring.”
Example: Use this in a security architecture document.
Meaning: It describes ongoing visibility across protected devices.
“EDR supports threat detection and investigation.”
Example: Use this in a cybersecurity project proposal.
Meaning: It summarizes two major security operations functions.
“Endpoint telemetry supports security investigations.”
Example: Use this in an incident response plan.
Meaning: It explains how endpoint data contributes to analysis.
“EDR can help security teams identify suspicious behavior.”
Example: Use this in an executive security briefing.
Meaning: It presents behavioral detection in clear business language.
“Response capabilities can help contain endpoint threats.”
Example: Use this in a security operations report.
Meaning: It explains how response actions can limit exposure.
“Centralized endpoint visibility supports SOC operations.”
Example: Use this when describing security operations workflows.
Meaning: It connects endpoint telemetry with analyst activities.
“EDR can improve incident investigation workflows.”
Example: Use this in a cybersecurity strategy document.
Meaning: It highlights operational value.
“Endpoint data can provide valuable incident context.”
Example: Use this during an incident response discussion.
Meaning: It explains why analysts need detailed device information.
“EDR supports a more informed response process.”
Example: Use this when presenting endpoint security improvements.
Meaning: It emphasizes informed decision-making.
“Security teams can use endpoint telemetry to investigate alerts.”
Example: Use this in a technical security presentation.
Meaning: It explains how alerts connect to investigation.
“EDR complements broader security controls.”
Example: Use this in an enterprise security architecture discussion.
Meaning: It clarifies that EDR is one component of a larger security strategy.
“Endpoint monitoring strengthens visibility across distributed devices.”
Example: Use this when discussing remote or hybrid environments.
Meaning: It highlights the value of centralized endpoint awareness.
EDR Detection And Monitoring Responses
“Watch the endpoint, then investigate the signal.”
Example: Use this when describing an EDR monitoring workflow.
Meaning: It connects detection with follow-up investigation.
“Continuous monitoring creates more security context.”
Example: Use this in an endpoint security presentation.
Meaning: It explains why ongoing visibility matters.
“Detection starts with understanding normal behavior.”
Example: Use this when discussing behavioral analytics.
Meaning: It highlights the importance of recognizing deviations.
“Suspicious activity deserves context.”
Example: Use this when discussing alert investigation.
Meaning: It warns against interpreting alerts without supporting evidence.
“Not every alert tells the whole story.”
Example: Use this when explaining alert triage.
Meaning: It emphasizes the need for investigation.
“Endpoint signals become useful when connected.”
Example: Use this when explaining event correlation.
Meaning: It highlights the value of combining related activity.
“Monitor processes, users, connections, and changes.”
Example: Use this when outlining endpoint telemetry categories.
Meaning: It summarizes different types of activity security teams may examine.
“Visibility helps analysts investigate what happened.”
Example: Use this when explaining EDR investigation.
Meaning: It connects monitoring with incident understanding.
“Good detection creates a path to investigation.”
Example: Use this when discussing security workflows.
Meaning: It links alerts to actionable analysis.
“Behavior can reveal what signatures miss.”
Example: Use this when explaining behavior-based detection.
Meaning: It highlights an important EDR detection approach.
“Context turns alerts into investigations.”
Example: Use this in a SOC training session.
Meaning: It explains why surrounding activity matters.
“Monitoring is valuable when it leads to action.”
Example: Use this when discussing security operations maturity.
Meaning: It emphasizes practical response over passive visibility.
EDR Threat Investigation Ideas
“Start with the suspicious event.”
Example: Use this when outlining an investigation process.
Meaning: It establishes the initial point of analysis.
“Follow the activity around the alert.”
Example: Use this when teaching analysts how to investigate endpoint events.
Meaning: It encourages examining surrounding context.
“Look for related processes and connections.”
Example: Use this when investigating suspicious endpoint behavior.
Meaning: It directs attention toward connected activity.
“Build the timeline before drawing conclusions.”
Example: Use this during incident analysis.
Meaning: It encourages evidence-based investigation.
“Ask what happened before the alert.”
Example: Use this when examining a suspicious event.
Meaning: It encourages analysts to establish a sequence of events.
“Ask what happened after the alert.”
Example: Use this when reviewing endpoint activity.
Meaning: It helps identify possible follow-on behavior.
“The timeline can tell the story.”
Example: Use this when explaining endpoint investigation.
Meaning: It highlights chronological analysis.
“Investigate the process, user, and device context.”
Example: Use this when triaging endpoint alerts.
Meaning: It identifies important investigation dimensions.
“Correlate related endpoint events.”
Example: Use this when discussing incident analysis.
Meaning: It encourages connecting separate observations.
“Separate the signal from the noise.”
Example: Use this when explaining alert triage.
Meaning: It describes the need to distinguish meaningful activity from benign events.
“Evidence should drive the investigation.”
Example: Use this when training security analysts.
Meaning: It encourages objective analysis.
“Document the timeline as you investigate.”
Example: Use this during incident response preparation.
Meaning: It supports clear records and later review.
EDR Endpoint Response Strategies
“Detect it, investigate it, contain it.”
Example: Use this as a simple endpoint response framework.
Meaning: It presents a practical sequence for handling suspicious activity.
“Response should match the level of risk.”
Example: Use this when discussing incident prioritization.
Meaning: It emphasizes proportional response.
“Containment can limit further exposure.”
Example: Use this in an incident response presentation.
Meaning: It explains the purpose of containment.
“Investigate before taking disruptive action when appropriate.”
Example: Use this when discussing response planning.
Meaning: It highlights the need to balance evidence gathering with containment.
“Endpoint isolation can be part of containment.”
Example: Use this when explaining response capabilities.
Meaning: It describes one possible response measure.
“Response decisions need context.”
Example: Use this when discussing automated or manual response.
Meaning: It emphasizes informed action.
“Containment is not the same as recovery.”
Example: Use this when explaining incident response stages.
Meaning: It distinguishes stopping an issue from restoring normal operations.
“A response plan should define who acts and when.”
Example: Use this when creating security procedures.
Meaning: It emphasizes clear responsibilities.
“Document response actions as they happen.”
Example: Use this during incident management.
Meaning: It supports accountability and later review.
“Coordinate endpoint response with incident response.”
Example: Use this in an enterprise security plan.
Meaning: It connects endpoint actions with broader incident management.
“Fast response matters, but context matters too.”
Example: Use this when discussing response automation.
Meaning: It balances speed with informed decisions.
“Recovery begins after containment and investigation.”
Example: Use this when explaining the broader response lifecycle.
Meaning: It separates recovery from immediate containment.
EDR For Cybersecurity Teams
“Give analysts better endpoint visibility.”
Example: Use this when presenting EDR to a SOC team.
Meaning: It focuses on improving analyst awareness.
“Centralize endpoint investigation.”
Example: Use this when discussing security operations workflows.
Meaning: It describes bringing endpoint evidence into a unified workflow.
“Reduce investigation guesswork.”
Example: Use this when explaining the value of endpoint telemetry.
Meaning: It highlights evidence-based analysis.
“Connect alerts with endpoint activity.”
Example: Use this when discussing security monitoring integration.
Meaning: It helps analysts understand why an alert occurred.
“Give the SOC more context.”
Example: Use this when presenting endpoint detection capabilities.
Meaning: It emphasizes information needed for investigation.
“Make endpoint events easier to investigate.”
Example: Use this when discussing security operations efficiency.
Meaning: It focuses on analyst usability.
“Improve visibility across managed endpoints.”
Example: Use this when discussing enterprise device coverage.
Meaning: It emphasizes broad monitoring.
“Support faster security investigations.”
Example: Use this when explaining operational benefits.
Meaning: It connects endpoint data with investigation efficiency.
“Bring endpoint evidence into the incident workflow.”
Example: Use this when designing SOC processes.
Meaning: It connects endpoint telemetry to incident handling.
“Turn endpoint telemetry into actionable context.”
Example: Use this when discussing security analytics.
Meaning: It emphasizes practical use of collected data.
“Make security alerts easier to understand.”
Example: Use this when explaining contextual detection.
Meaning: It focuses on reducing ambiguity.
“Build investigations around evidence.”
Example: Use this when training analysts.
Meaning: It encourages structured, evidence-based analysis.
EDR Endpoint Detection Response For Businesses
“Protect the devices employees depend on.”
Example: Use this when presenting endpoint security to business leaders.
Meaning: It connects cybersecurity with daily operations.
“Endpoint security supports business continuity.”
Example: Use this when discussing organizational resilience.
Meaning: It connects device protection with operational stability.
“Visibility helps organizations understand endpoint risk.”
Example: Use this in a risk management presentation.
Meaning: It explains why endpoint awareness matters to businesses.
“Security teams need visibility beyond the network edge.”
Example: Use this when discussing distributed work environments.
Meaning: It highlights endpoint importance.
“Remote work makes endpoint visibility more important.”
Example: Use this when discussing distributed device environments.
Meaning: It connects endpoint monitoring with modern work patterns.
“A compromised endpoint can create wider security concerns.”
Example: Use this in an executive security briefing.
Meaning: It explains why individual devices matter.
“EDR can support centralized security operations.”
Example: Use this when presenting enterprise security architecture.
Meaning: It highlights operational integration.
“Endpoint telemetry can support incident investigations.”
Example: Use this when explaining business security processes.
Meaning: It identifies a practical use of endpoint data.
“Security visibility supports informed decisions.”
Example: Use this when discussing cybersecurity investments.
Meaning: It connects data with decision-making.
“Strong endpoint controls can complement broader defenses.”
Example: Use this when explaining layered security.
Meaning: It positions endpoint protection within a larger strategy.
“Business risk and endpoint risk are connected.”
Example: Use this when discussing enterprise risk management.
Meaning: It shows how technical issues can affect operations.
“Cybersecurity works better as a coordinated system.”
Example: Use this when discussing multiple security controls.
Meaning: It emphasizes defense-in-depth thinking.
EDR Endpoint Detection Response For Remote Work
“Every remote device is part of the security picture.”
Example: Use this when explaining remote workforce security.
Meaning: It highlights endpoint importance outside the office.
“The office moved, but security still has to follow.”
Example: Use this in a remote-work security presentation.
Meaning: It explains why endpoint controls must support distributed environments.
“Remote endpoints need consistent visibility.”
Example: Use this when discussing security monitoring across home devices.
Meaning: It emphasizes centralized awareness.
“Distance should not mean less security context.”
Example: Use this when explaining remote endpoint monitoring.
Meaning: It highlights the need for visibility regardless of location.
“Home networks still connect to business workflows.”
Example: Use this when discussing remote employees.
Meaning: It explains why remote endpoints can matter to organizations.
“Endpoint protection travels with the workforce.”
Example: Use this when describing mobile or remote security.
Meaning: It emphasizes security beyond office boundaries.
“Remote work expands the endpoint conversation.”
Example: Use this when discussing distributed security architecture.
Meaning: It highlights how workplace changes affect endpoint strategy.
“Visibility matters wherever the device goes.”
Example: Use this in an endpoint security awareness campaign.
Meaning: It emphasizes location-independent monitoring.
“Secure remote work starts with managed endpoints.”
Example: Use this when discussing endpoint security foundations.
Meaning: It highlights the role of endpoint management.
“Remote access increases the need for context.”
Example: Use this when discussing distributed access patterns.
Meaning: It emphasizes understanding endpoint activity.
“Distributed teams need distributed endpoint visibility.”
Example: Use this when presenting remote security requirements.
Meaning: It connects workforce distribution with monitoring needs.
“The endpoint is still part of the perimeter.”
Example: Use this when explaining modern security models.
Meaning: It highlights the importance of device-level security.
EDR And Incident Response
“EDR can provide useful evidence during an incident.”
Example: Use this when explaining how endpoint data supports investigations.
Meaning: It connects endpoint telemetry with incident response.
“Start the investigation with the available endpoint evidence.”
Example: Use this when responding to a suspicious device event.
Meaning: It encourages evidence-based analysis.
“Build the incident timeline from endpoint activity.”
Example: Use this during forensic investigation planning.
Meaning: It highlights chronological analysis.
“Contain affected endpoints when appropriate.”
Example: Use this when discussing incident containment procedures.
Meaning: It describes a possible way to limit ongoing exposure.
“Document every important response action.”
Example: Use this when creating incident response procedures.
Meaning: It supports accountability and post-incident review.
“Connect endpoint findings with the wider incident.”
Example: Use this when analyzing a multi-stage security event.
Meaning: It encourages broader contextual investigation.
“Use endpoint evidence to validate assumptions.”
Example: Use this during incident analysis.
Meaning: It promotes evidence-based conclusions.
“Do not investigate an endpoint in isolation.”
Example: Use this when discussing complex incidents.
Meaning: It encourages considering broader security context.
“Coordinate EDR findings with the response team.”
Example: Use this during collaborative incident handling.
Meaning: It encourages cross-team communication.
“Record what changed, when, and why.”
Example: Use this when documenting endpoint response actions.
Meaning: It creates a clearer incident record.
“Containment buys time for deeper investigation.”
Example: Use this when explaining incident response sequencing.
Meaning: It describes the relationship between containment and analysis.
“Learn from every endpoint incident.”
Example: Use this during post-incident review.
Meaning: It connects incidents with future security improvements.
EDR Endpoint Detection Response Benefits
“Better visibility can improve threat awareness.”
Example: Use this when presenting the value of EDR to stakeholders.
Meaning: It highlights increased endpoint awareness.
“Detailed endpoint data can support investigations.”
Example: Use this when discussing forensic workflows.
Meaning: It explains how telemetry can aid analysis.
“Centralized monitoring can simplify security operations.”
Example: Use this when discussing SOC workflows.
Meaning: It highlights operational organization.
“Faster access to endpoint context can support response.”
Example: Use this when explaining incident handling.
Meaning: It connects information availability with response work.
“Behavior-based detection can identify suspicious patterns.”
Example: Use this when explaining detection approaches.
Meaning: It describes how unusual activity can become a security signal.
“Historical data can help reconstruct incidents.”
Example: Use this during a forensic investigation discussion.
Meaning: It explains the value of retained endpoint evidence.
“Endpoint visibility supports threat hunting.”
Example: Use this when discussing proactive security analysis.
Meaning: It connects endpoint telemetry with hunting activities.
“Response capabilities can help limit endpoint exposure.”
Example: Use this when discussing containment.
Meaning: It describes the potential operational value of response actions.
“EDR can strengthen endpoint-focused security operations.”
Example: Use this when comparing security capabilities.
Meaning: It summarizes the role of EDR.
“Security teams gain another source of investigation data.”
Example: Use this when discussing layered monitoring.
Meaning: It highlights the value of endpoint evidence.
“Endpoint data can improve incident context.”
Example: Use this when presenting EDR benefits.
Meaning: It explains how endpoint visibility supports understanding.
“Better context can help analysts prioritize investigations.”
Example: Use this when discussing alert triage.
Meaning: It connects endpoint information with analyst decision-making.
EDR Endpoint Detection Response Challenges
“More visibility can also mean more data.”
Example: Use this when discussing EDR deployment challenges.
Meaning: It highlights the need to manage telemetry volume.
“Alert fatigue can become a serious operational issue.”
Example: Use this when discussing security analyst workloads.
Meaning: It explains why alert quality matters.
“Not every endpoint event represents a threat.”
Example: Use this when explaining alert triage.
Meaning: It emphasizes the need to distinguish benign behavior from suspicious activity.
“EDR still needs skilled analysis.”
Example: Use this when discussing security team requirements.
Meaning: It shows that technology does not eliminate human judgment.
“Poor configuration can reduce useful visibility.”
Example: Use this when reviewing endpoint security deployment.
Meaning: It highlights the importance of configuration quality.
“Coverage matters as much as capability.”
Example: Use this when evaluating endpoint protection.
Meaning: It emphasizes the importance of protecting relevant devices.
“Response actions need careful governance.”
Example: Use this when discussing automated response.
Meaning: It highlights operational and business considerations.
“Telemetry retention should match investigation needs.”
Example: Use this when planning endpoint data storage.
Meaning: It connects retention decisions with investigative requirements.
“Integration can affect operational efficiency.”
Example: Use this when evaluating security architecture.
Meaning: It recognizes the importance of connecting EDR with other workflows.
“A security tool is only useful when teams can use it well.”
Example: Use this when discussing EDR implementation.
Meaning: It emphasizes training and operational readiness.
“Endpoint visibility needs ongoing management.”
Example: Use this when planning long-term security operations.
Meaning: It shows that EDR is not simply a set-and-forget technology.
“Security teams should review detection quality regularly.”
Example: Use this during security program improvement discussions.
Meaning: It encourages continuous tuning and evaluation.
EDR Best Practices And Smart Usage
“Define what endpoints need protection.”
Example: Use this before planning an EDR rollout.
Meaning: It establishes the required security scope.
“Start with clear detection goals.”
Example: Use this when designing an endpoint security strategy.
Meaning: It creates measurable objectives.
“Tune alerts around real operational needs.”
Example: Use this when reducing unnecessary alerts.
Meaning: It improves the usefulness of security notifications.
“Keep endpoint coverage visible.”
Example: Use this during security program reviews.
Meaning: It helps teams understand where protection exists.
“Document response procedures.”
Example: Use this when building incident response playbooks.
Meaning: It creates clearer actions for security teams.
“Test response workflows regularly.”
Example: Use this when validating incident readiness.
Meaning: It helps identify process gaps before real incidents.
“Train analysts on endpoint investigation.”
Example: Use this when building SOC capabilities.
Meaning: It develops human expertise alongside technology.
“Review detection rules and policies.”
Example: Use this during regular security maintenance.
Meaning: It encourages continuous improvement.
“Connect EDR with the wider security strategy.”
Example: Use this when planning enterprise security architecture.
Meaning: It prevents endpoint security from operating in isolation.
“Measure useful outcomes, not just alert volume.”
Example: Use this when evaluating security performance.
Meaning: It focuses measurement on practical results.
“Keep response decisions documented.”
Example: Use this during incident management reviews.
Meaning: It improves accountability and learning.
“Improve the process after every major incident.”
Example: Use this during post-incident reviews.
Meaning: It turns experience into future security improvements.
FAQs
What does EDR endpoint detection response mean?
EDR endpoint detection response refers to security capabilities focused on monitoring endpoints, detecting suspicious activity, investigating potential threats, and supporting response actions.
Is EDR the same as antivirus?
Not exactly. Traditional antivirus primarily focuses on preventing and detecting malicious software, while EDR generally provides broader endpoint visibility, investigation, behavioral detection, and response capabilities.
What does EDR monitor?
Depending on the product and configuration, EDR can collect information about processes, files, users, network activity, system changes, and other endpoint events.
Is EDR useful for businesses?
Yes. EDR can help organizations improve endpoint visibility, investigate suspicious activity, support incident response, and understand security events across managed devices.
Can EDR detect suspicious behavior?
Yes. EDR technologies can use behavioral analysis and other detection methods to identify activity that may indicate malicious or unusual behavior.
Is EDR only for large companies?
No. EDR can be relevant to organizations of different sizes. The appropriate solution depends on factors such as endpoint count, security requirements, available staff, budget, and operational needs.
Can EDR help with incident response?
Yes. Endpoint telemetry can provide useful evidence for investigation, while response capabilities can support containment and other incident-handling actions.
Is EDR completely automated?
Not necessarily. Some EDR platforms support automation, but security teams may still need to investigate alerts, validate findings, make response decisions, and manage incidents.
What should you look for in an EDR solution?
Important considerations can include endpoint coverage, detection capabilities, investigation features, response options, telemetry quality, integrations, usability, reporting, and operational requirements.
Can EDR replace all other cybersecurity tools?
Usually, EDR should be viewed as one component of a broader security strategy. Organizations may also use identity security, network controls, email security, vulnerability management, backup systems, and other defenses.
Is humor appropriate when explaining EDR?
Humor can make cybersecurity topics more engaging and memorable, but technical and incident communications should remain professional and appropriate.
Conclusion
EDR endpoint detection response may sound like another complicated cybersecurity acronym, but the basic idea is straightforward: understand what is happening on endpoints, identify suspicious activity, investigate the evidence, and support an appropriate response. The strongest EDR strategy combines technology with skilled analysts, clear processes, useful telemetry, and regular improvement.
Whether you are explaining endpoint security to a business team, creating cybersecurity content, planning a security program, or learning the basics yourself, the right wording can make a technical topic much easier to understand. Use these examples as inspiration, adapt them to your audience, and keep the message clear. Save this guide for your next cybersecurity project, share it with your team, and keep building smarter endpoint security conversations.