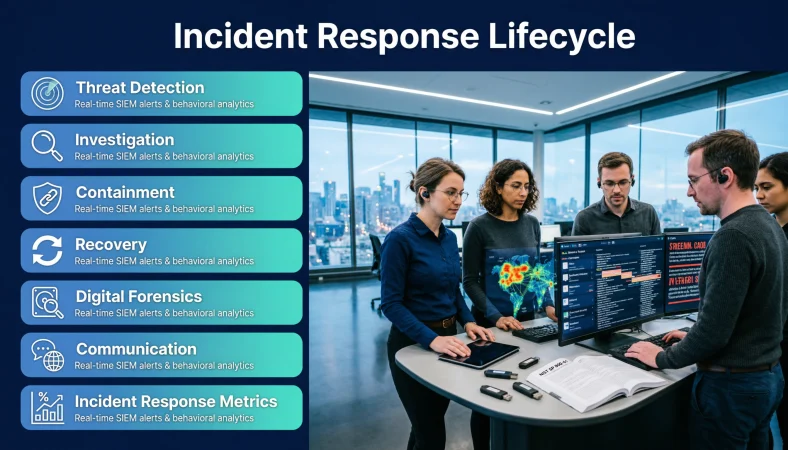
An incident response team cybersecurity function helps organizations detect, investigate, contain, and recover from security incidents such as ransomware, phishing, and data breaches. The team combines technical expertise, clear communication, and established procedures to reduce damage and restore normal operations.
Top alternatives: Cybersecurity Incident Response Team, Computer Security Incident Response Team, CSIRT Roles and Responsibilities, Security Incident Management Team, Cybersecurity Incident Response Process
Cybersecurity incidents rarely arrive with a polite calendar invitation. One suspicious login, a phishing email, or an unexpected system alert can quickly become a serious business problem. That is where an incident response team cybersecurity function becomes essential.
These teams help organizations understand what happened, limit the impact, preserve evidence, and recover safely. Whether you work in IT, study cybersecurity, manage a business, or simply want to understand how digital defenses work, knowing how incident response teams operate gives you a clearer picture of modern security.
The right people, procedures, and communication can make a major difference when every minute matters. From defining team roles to building response plans and practicing realistic scenarios, this guide covers the essentials in straightforward language without turning cybersecurity into a wall of technical jargon.
Understanding an Incident Response Team in Cybersecurity
Detecting and Investigating Security Threats
1. A Team Built for Security Incidents
Example: Use this description when introducing a dedicated team responsible for handling suspected cyberattacks.
Meaning: The team coordinates the investigation and response when a security incident occurs.
2. Detect Threats Early
Example: Include this responsibility when explaining how analysts monitor alerts and unusual account activity.
Meaning: Early detection helps the organization respond before an incident causes greater damage.
3. Investigate Suspicious Activity
Example: Describe the team reviewing authentication records after several unusual login attempts.
Meaning: Investigation helps establish what happened and whether a genuine security incident occurred.
Containing Threats and Restoring Systems
4. Contain the Threat
Example: Explain how authorized responders may isolate a compromised device under an approved plan.
Meaning: Containment limits the spread or impact of malicious activity.
5. Remove the Cause
Example: Include the process of removing confirmed malware or closing an exploited vulnerability.
Meaning: Eradication addresses the threat that caused the incident.
6. Restore Normal Operations
Example: Describe restoring affected services after systems have been checked and approved for recovery.
Meaning: Recovery returns systems to a safe and functional state.
Preserving Evidence and Coordinating Teams
7. Preserve Digital Evidence
Example: Mention the secure collection of relevant logs and forensic artifacts during an investigation.
Meaning: Evidence helps establish the incident timeline and supports further analysis.
8. Coordinate Technical Specialists
Example: Describe analysts working with network engineers, system administrators, and forensic specialists.
Meaning: Different areas of expertise help the team understand and resolve complex incidents.
9. Communicate With Leadership
Example: Include a concise incident briefing that explains business impact and response progress.
Meaning: Decision-makers need accurate information to support appropriate actions.
Protecting Operations and Improving Response
10. Protect Business Operations
Example: Explain how responders prioritize systems that support essential services.
Meaning: The team considers operational consequences alongside technical risks.
11. Document Every Major Action
Example: Record important decisions, investigation findings, and recovery milestones in the incident log.
Meaning: Documentation supports accountability, coordination, and future improvement.
12. Learn From Every Incident
Example: Review a completed investigation to identify gaps in controls or response procedures.
Meaning: Lessons learned help reduce the chance of similar incidents happening again.
Incident Response Team Roles and Responsibilities
Incident Leadership and Investigation Roles
1. Incident Response Manager
Example: Assign this role to coordinate the response, track priorities, and manage major decisions.
Meaning: The manager keeps the response organized and aligned with the incident plan.
2. Security Analyst
Example: Include analysts who review alerts, examine logs, and identify suspicious patterns.
Meaning: Analysts help establish whether activity represents a genuine threat.
3. Incident Handler
Example: Describe specialists who follow response procedures and coordinate investigation tasks.
Meaning: Incident handlers help move the incident from detection toward resolution.
Forensics and Technical Security Specialists
4. Digital Forensics Specialist
Example: Assign forensic specialists to examine relevant devices, files, and system artifacts.
Meaning: They help reconstruct events and preserve useful evidence.
5. Threat Intelligence Analyst
Example: Include a specialist who checks suspicious indicators against reliable threat intelligence.
Meaning: Threat intelligence can provide context about possible attackers and their methods.
6. Network Security Engineer
Example: Ask network specialists to investigate unusual traffic and implement approved network controls.
Meaning: They help identify and limit threats moving through network infrastructure.
Endpoint, Cloud, and IT Operations Roles
7. Endpoint Security Specialist
Example: Include personnel who investigate suspicious processes and endpoint protection alerts.
Meaning: They help determine whether individual devices have been compromised.
8. Cloud Security Specialist
Example: Assign cloud expertise when an incident involves cloud accounts, workloads, or configurations.
Meaning: The specialist understands the platform-specific evidence and controls.
9. IT Operations Representative
Example: Involve system administrators when affected services require technical changes or recovery.
Meaning: IT operations helps restore systems without overlooking dependencies.
Legal, Communications, and Executive Responsibilities
10. Legal Representative
Example: Include legal counsel when an incident may trigger contractual, regulatory, or litigation concerns.
Meaning: Legal guidance helps the organization understand its obligations.
11. Communications Representative
Example: Assign an authorized spokesperson to prepare approved internal or public updates.
Meaning: Coordinated messaging reduces confusion and unsupported claims.
12. Executive Decision-Maker
Example: Identify the person authorized to approve major business decisions during a severe incident.
Meaning: Clear authority helps resolve decisions that extend beyond technical response.
Incident Response Team Cybersecurity Skills
Core Technical Investigation Skills
1. Log Analysis
Example: Demonstrate how you connect authentication events with endpoint and network records.
Meaning: Log analysis helps reveal suspicious behavior and establish an incident timeline.
2. Network Fundamentals
Example: Practice identifying unusual DNS requests, connections, and traffic patterns in a lab.
Meaning: Networking knowledge helps responders understand how systems communicate.
3. Endpoint Investigation
Example: Review process activity and security alerts in a controlled training environment.
Meaning: Endpoint analysis helps identify possible compromise on individual devices.
Security Monitoring and Forensic Skills
4. SIEM Experience
Example: Practice searching and correlating security events in a security information and event management platform.
Meaning: SIEM skills help analysts investigate alerts from multiple sources.
5. EDR Familiarity
Example: Learn how endpoint detection and response platforms investigate suspicious activity.
Meaning: EDR knowledge supports threat detection and endpoint containment.
6. Digital Forensics
Example: Practice preserving sample evidence and recording its handling in a training lab.
Meaning: Forensic skills help maintain the reliability of investigation findings.
Automation, Cloud Security, and Threat Research
7. Scripting and Automation
Example: Write a basic Python script to organize sample indicators from a log file.
Meaning: Automation can reduce repetitive tasks and improve consistency.
8. Cloud Security Knowledge
Example: Examine sample cloud audit logs and investigate unusual account activity.
Meaning: Cloud knowledge helps teams respond to incidents outside traditional on-premises systems.
9. Threat Intelligence Research
Example: Review reliable reports to understand the context of a suspicious domain or file hash.
Meaning: Intelligence can help prioritize and interpret potential threats.
Documentation, Risk Assessment, and Communication
10. Incident Documentation
Example: Prepare a report with a timeline, affected systems, actions taken, and unresolved questions.
Meaning: Clear records help other responders understand the investigation.
11. Risk Assessment
Example: Compare the likely impact of a compromised public server with that of an isolated test machine.
Meaning: Risk assessment helps determine response priorities.
12. Communication Under Pressure
Example: Explain an incident’s technical status and business impact in a short briefing.
Meaning: Clear communication supports timely decisions during stressful situations.
Incident Response Team Cybersecurity Tools
Security Monitoring and Threat Detection Tools
1. Security Information and Event Management Platforms
Example: Use a SIEM platform to correlate authentication events, network alerts, and endpoint records.
Meaning: SIEM technology helps analysts identify patterns across security data.
2. Endpoint Detection and Response Platforms
Example: Review endpoint alerts and process activity using an approved EDR platform.
Meaning: EDR tools support investigation and response on individual devices.
3. Network Monitoring Tools
Example: Examine network traffic metadata to investigate unexpected connections.
Meaning: Network tools help reveal suspicious communication between systems.
Investigation and Threat Intelligence Tools
4. Digital Forensics Software
Example: Use approved forensic software to examine a properly collected disk image.
Meaning: Forensic tools help investigators analyze digital evidence.
5. Threat Intelligence Platforms
Example: Check an indicator against trusted intelligence sources during an investigation.
Meaning: These platforms add context to suspicious technical findings.
6. Case Management Systems
Example: Track incident tasks, assigned owners, evidence references, and response deadlines.
Meaning: Case management keeps investigations organized and auditable.
Communication and Security Assessment Tools
7. Secure Communication Channels
Example: Use an approved incident channel that remains available if ordinary business systems are affected.
Meaning: Reliable communications help responders coordinate safely.
8. Vulnerability Scanners
Example: Review authorized scan results to determine whether an incident involves a known weakness.
Meaning: Vulnerability information can help identify potential entry points.
9. Malware Analysis Environments
Example: Examine suspicious files in a properly isolated analysis environment managed by trained personnel.
Meaning: Safe analysis helps determine the behavior and risk of suspected malware.
Recovery, Identity, and Reporting Tools
10. Backup and Recovery Systems
Example: Verify backup integrity before using backups to restore affected services.
Meaning: Reliable recovery systems can help restore operations after an incident.
11. Identity Security Tools
Example: Review account activity and access permissions during a suspected credential compromise.
Meaning: Identity tools help teams investigate account misuse and restrict unauthorized access.
12. Reporting Dashboards
Example: Use an approved dashboard to track incident status, affected assets, and response milestones.
Meaning: Dashboards give the team a shared view of progress and outstanding work.
Incident Response Team Cybersecurity Procedures
Preparation and Incident Identification
1. Prepare Before an Incident
Example: Maintain current response plans, contact lists, access arrangements, and recovery procedures.
Meaning: Preparation reduces confusion when an incident begins.
2. Identify the Incident
Example: Review alerts and available evidence to determine whether a security incident has occurred.
Meaning: Identification establishes the need for a coordinated response.
3. Assess Severity
Example: Evaluate affected systems, data sensitivity, business disruption, and signs of ongoing compromise.
Meaning: Severity assessment helps prioritize resources and escalation.
Activating the Team and Containing Threats
4. Activate the Response Team
Example: Notify the designated incident lead when an event meets the organization’s activation criteria.
Meaning: Activation brings the necessary people into the response process.
5. Establish a Timeline
Example: Record when the event began, when it was detected, and what actions followed.
Meaning: A timeline helps responders reconstruct events and evaluate progress.
6. Contain the Incident
Example: Apply approved isolation or access restrictions to limit further damage.
Meaning: Containment reduces exposure while the team investigates.
Evidence Preservation and System Recovery
7. Preserve Evidence
Example: Follow forensic procedures for relevant logs, files, and system records.
Meaning: Proper evidence handling supports reliable analysis.
8. Eradicate the Threat
Example: Remove confirmed malicious components and address the vulnerabilities that enabled the incident.
Meaning: Eradication aims to eliminate the cause of compromise.
9. Recover Affected Systems
Example: Restore services using verified backups and approved recovery procedures.
Meaning: Recovery returns systems to operation while managing remaining risks.
Security Validation and Continuous Improvement
10. Validate System Security
Example: Check restored services for unresolved indicators and verify that required controls are functioning.
Meaning: Validation reduces the risk of returning compromised systems to production.
11. Communicate Status Updates
Example: Provide scheduled updates to authorized stakeholders using verified information.
Meaning: Regular communication keeps everyone informed without spreading speculation.
12. Complete a Post-Incident Review
Example: Document root causes, response gaps, corrective actions, and responsible owners.
Meaning: Review turns the incident into an opportunity to improve security.
Incident Response Team Cybersecurity Communication Examples
Initial Alerts and Incident Escalation
1. Initial Incident Notification
Example: Use this message when notifying the designated security contact about a suspected incident.
Meaning: It communicates the essential facts without overstating what is known.
Suggested wording: “A potential security incident has been identified at [time]. The affected systems and scope are being assessed. The designated response team has been notified.”
2. Suspicious Login Alert
Example: Use this when reporting unusual authentication activity to the security team.
Meaning: It flags activity that requires investigation.
Suggested wording: “Unusual login activity was detected for [account or system] at [time]. Please review the event and follow the approved escalation process.”
3. Possible Phishing Report
Example: Use this when an employee reports a suspicious email.
Meaning: It records the concern without assuming the message is confirmed malicious.
Suggested wording: “A potentially suspicious email has been reported. Please review the message through the approved security reporting process and avoid interacting with its contents until advised.”
Escalation and Protective Actions
4. Incident Escalation Notice
Example: Use this when an incident exceeds the authority or capability of the initial responder.
Meaning: It ensures the appropriate specialists and decision-makers are involved.
Suggested wording: “The incident requires additional assessment due to its potential impact on [system or service]. Escalation has been requested under the incident response plan.”
5. Executive Status Update
Example: Use this when leadership needs a concise summary of a developing incident.
Meaning: It highlights business impact, current actions, and outstanding decisions.
Suggested wording: “The team is investigating a security incident affecting [service]. Containment and impact assessment are underway. Confirmed findings and next steps will be shared as they become available.”
6. System Isolation Notice
Example: Use this after authorized responders decide to isolate an affected system.
Meaning: It informs relevant teams about a protective action.
Suggested wording: “System [identifier] has been isolated under the approved response procedure while the investigation continues. Please coordinate any related operational changes with the incident lead.”
Service Updates and Investigation Support
7. Service Disruption Update
Example: Use this when an incident affects a business application or customer service.
Meaning: It explains the disruption without exposing sensitive investigation details.
Suggested wording: “We are investigating a security-related disruption affecting [service]. The team is working to assess the impact and restore normal operation safely.”
8. Evidence Preservation Request
Example: Use this when asking authorized staff to preserve relevant records.
Meaning: It helps prevent the loss of information needed for the investigation.
Suggested wording: “Please preserve relevant logs and records for [system or timeframe] according to the incident response procedure. Do not alter or delete potentially relevant evidence.”
9. Request for Technical Support
Example: Use this when the response team needs help from infrastructure or application specialists.
Meaning: It clarifies the support needed to investigate or resolve the incident.
Suggested wording: “The incident response team requests technical assistance with [system or issue]. Please coordinate with [incident lead] before making changes to the affected environment.”
Recovery, Closure, and Continuous Improvement
10. Recovery Status Update
Example: Use this when responders have begun authorized recovery activities.
Meaning: It gives stakeholders a factual update without promising an unverified completion time.
Suggested wording: “Recovery activities for [service] are underway. The team is validating system integrity and will provide an update when the next milestone is confirmed.”
11. Incident Closure Summary
Example: Use this after the incident lead confirms that response activities meet closure criteria.
Meaning: It records the outcome and any remaining follow-up work.
Suggested wording: “The response team has completed the primary actions for [incident]. Outstanding corrective actions will be tracked separately, and the final incident record will document verified findings.”
12. Post-Incident Lessons Learned
Example: Use this when presenting recommendations after an investigation.
Meaning: It focuses on improvement rather than blame.
Suggested wording: “The review identified opportunities to improve detection, communication, and recovery readiness. Action owners and target dates will be documented in the follow-up plan.”
Incident Response Team Cybersecurity Frameworks
Core Cybersecurity Standards and Guidance
1. NIST Incident Response Guidance
Example: Review NIST guidance when developing or improving an organization’s incident response approach.
Meaning: NIST publications provide structured recommendations for cybersecurity risk management and incident response.
2. NIST Cybersecurity Framework 2.0
Example: Use the framework to connect incident response planning with broader organizational cybersecurity risk management.
Meaning: It helps organizations organize security outcomes across governance, protection, detection, response, and recovery.
3. ISO/IEC 27001
Example: Consider the standard when managing an information security management system.
Meaning: It provides requirements for establishing and improving an information security management system.
Incident Management and Threat Analysis Frameworks
4. ISO/IEC 27035
Example: Review the incident management guidance when designing formal incident handling processes.
Meaning: The series addresses information security incident management.
5. MITRE ATT&CK
Example: Use ATT&CK techniques to describe observed adversary behavior in an investigation report.
Meaning: It provides a knowledge base of tactics and techniques used by attackers.
6. Cyber Kill Chain
Example: Use the model as one way to discuss stages of certain cyberattacks.
Meaning: It can help teams structure discussions about attacker activity, although real incidents do not always follow a neat sequence.
Team Services and Operational Procedures
7. FIRST CSIRT Services Framework
Example: Review the framework when defining services offered by a computer security incident response team.
Meaning: It helps organizations describe and organize CSIRT capabilities.
8. Incident Classification Standards
Example: Define consistent categories for malware, phishing, unauthorized access, and service disruption.
Meaning: Classification improves triage and reporting consistency.
9. Internal Incident Playbooks
Example: Develop an approved playbook for recurring scenarios such as compromised accounts.
Meaning: Playbooks guide responders through repeatable tasks and decision points.
Business Recovery and Compliance Requirements
10. Business Continuity Planning
Example: Coordinate incident response with plans for maintaining essential business services.
Meaning: Cybersecurity recovery often depends on wider operational continuity.
11. Disaster Recovery Planning
Example: Align security incident procedures with tested restoration plans for critical systems.
Meaning: Disaster recovery supports the return of systems and data after disruption.
12. Regulatory and Contractual Requirements
Example: Review applicable notification deadlines and contractual duties with qualified legal or compliance staff.
Meaning: Reporting obligations vary by jurisdiction, industry, and incident circumstances.
Incident Response Team Cybersecurity Scenarios
Email and Identity-Based Threat Scenarios
1. Phishing Campaign
Example: Simulate employees reporting a suspicious email that appears to come from a trusted supplier.
Meaning: The team practices validating the message, assessing exposure, and coordinating any necessary response.
2. Ransomware Detection
Example: Use a tabletop exercise involving suspicious file changes and an alert on a critical server.
Meaning: The team rehearses escalation, containment decisions, communication, and recovery planning.
3. Compromised Employee Account
Example: Practice investigating unusual sign-ins and unexpected changes to account permissions.
Meaning: The scenario tests identity investigation and access containment.
Data Exposure and Cloud Security Scenarios
4. Data Exfiltration Concern
Example: Review a simulated alert showing unusual outbound data transfers.
Meaning: Responders practice assessing potential data exposure and preserving evidence.
5. Cloud Account Misuse
Example: Use a scenario involving an unexpected cloud configuration change.
Meaning: The team practices investigating cloud audit records and limiting unauthorized access.
6. Lost Company Device
Example: Rehearse the response to a missing laptop that may contain business information.
Meaning: The scenario tests device reporting, access protection, and data risk assessment.
Infrastructure and Third-Party Incident Scenarios
7. Third-Party Security Incident
Example: Simulate a supplier notifying the organization of a breach that may affect shared services.
Meaning: The team practices coordination, impact assessment, and communication across organizations.
8. Denial-of-Service Attack
Example: Review a scenario in which an internet-facing service experiences a sudden traffic surge.
Meaning: The team practices determining impact and coordinating with network and service providers.
9. Privileged Account Compromise
Example: Investigate simulated evidence of suspicious activity involving an administrator account.
Meaning: The scenario tests high-priority identity controls and escalation procedures.
Operational Disruptions and Response Coordination
10. Security Monitoring Outage
Example: Practice responding when a key monitoring platform stops collecting events.
Meaning: The team assesses visibility gaps and alternative monitoring arrangements.
11. Accidental Data Exposure
Example: Simulate a case where a sensitive file becomes accessible to an unintended audience.
Meaning: Responders practice determining exposure, restricting access, and following reporting requirements.
12. Multiple Simultaneous Alerts
Example: Run an exercise with several alerts affecting different systems at the same time.
Meaning: The team practices prioritization, workload management, and coordination.
Incident Response Team Cybersecurity Metrics
Measuring Detection and Initial Response
1. Mean Time to Detect
Example: Track the time between the earliest identifiable malicious activity and its detection.
Meaning: This metric helps evaluate detection performance when the timestamps are reliable.
2. Mean Time to Acknowledge
Example: Measure how long it takes for an alert to receive initial attention.
Meaning: The metric shows how quickly the team begins reviewing reported activity.
3. Mean Time to Contain
Example: Record the time between incident confirmation and the completion of containment actions.
Meaning: This helps assess how quickly the team limits incident impact.
Evaluating Recovery and Incident Trends
4. Mean Time to Recover
Example: Track the time required to restore affected services to an approved operational state.
Meaning: The metric helps evaluate recovery performance.
5. Incident Volume
Example: Compare the number of confirmed incidents across reporting periods.
Meaning: Incident counts can show workload patterns but need context to be meaningful.
6. False Positive Rate
Example: Measure how many reviewed alerts are determined not to represent genuine threats.
Meaning: This can help teams evaluate alert quality and triage efficiency.
Assessing Response Quality and Evidence
7. Repeat Incident Rate
Example: Track recurring incidents linked to the same unresolved weakness.
Meaning: The metric can reveal whether corrective actions are effective.
8. Playbook Compliance
Example: Review whether required response steps were completed and documented.
Meaning: This helps assess consistency with approved procedures.
9. Evidence Completeness
Example: Check whether required evidence and investigation records are present in closed cases.
Meaning: Complete records support reliable analysis and later review.
Tracking Recovery Validation and Continuous Improvement
10. Recovery Validation Rate
Example: Track whether restored systems pass the organization’s required security checks.
Meaning: This helps measure the quality of recovery validation.
11. Training Exercise Results
Example: Record whether exercise objectives were met and whether assigned actions were completed.
Meaning: Exercise results show where response readiness needs improvement.
12. Corrective Action Completion
Example: Monitor overdue actions from post-incident reviews.
Meaning: This helps ensure lessons learned lead to practical improvements.
Building an Effective Incident Response Team Cybersecurity Program
Defining Team Roles and Responsibilities
1. Define the Team’s Scope
Example: Document which systems, locations, business units, and incident types the team supports.
Meaning: Clear scope helps establish responsibilities and avoid response gaps.
2. Assign Primary and Backup Roles
Example: Identify a backup incident lead for periods when the primary contact is unavailable.
Meaning: Coverage arrangements help maintain continuity.
3. Establish Escalation Thresholds
Example: Define when incidents require senior technical support or executive notification.
Meaning: Agreed thresholds help the team escalate consistently.
Preparing Systems and Response Procedures
4. Maintain a Current Asset Inventory
Example: Keep records of critical applications, servers, cloud services, and system owners.
Meaning: Asset information helps responders assess potential impact.
5. Map Critical Dependencies
Example: Document which services rely on shared identity systems, networks, or databases.
Meaning: Dependency information supports safer containment and recovery decisions.
6. Create Scenario-Based Playbooks
Example: Prepare approved response guides for common incident types.
Meaning: Playbooks make recurring tasks easier to coordinate.
Strengthening Recovery and Collaboration
7. Establish Secure Evidence Storage
Example: Define where investigation records and forensic artifacts must be stored.
Meaning: Secure storage helps protect sensitive information and maintain evidence integrity.
8. Test Backup and Recovery Plans
Example: Run authorized recovery tests rather than assuming backups will work during an emergency.
Meaning: Testing reveals issues before a real incident makes recovery urgent.
9. Coordinate With Business Teams
Example: Include service owners who can explain operational priorities and acceptable downtime.
Meaning: Technical actions should account for business consequences.
Building Long-Term Readiness and Improvement
10. Review External Support Options
Example: Identify when specialist incident response firms or legal advisers may be needed.
Meaning: Prearranged support can help address incidents beyond internal capabilities.
11. Track Improvement Actions
Example: Assign an owner and target date to each important lesson from an incident or exercise.
Meaning: Accountability helps ensure improvements are completed.
12. Reassess Program Readiness
Example: Review staffing, tools, procedures, and exercise results at planned intervals.
Meaning: Regular evaluation helps keep the response program effective as risks change.
Incident Response Team Cybersecurity Mistakes to Avoid
Common Incident Response Planning Mistakes
1. Treating Every Alert as a Confirmed Breach
Example: Validate the evidence before communicating that an attack has been confirmed.
Meaning: Accurate classification avoids unnecessary alarm and incorrect reporting.
2. Delaying Escalation
Example: Follow the escalation criteria when an incident affects critical systems or sensitive data.
Meaning: Timely escalation brings the right expertise into the response.
3. Making Unapproved Changes
Example: Coordinate system isolation or configuration changes through the incident lead and approved procedures.
Meaning: Uncoordinated actions can disrupt services or destroy useful evidence.
Assessing Impact and Protecting Evidence
4. Ignoring Business Impact
Example: Include service criticality and customer consequences when assessing incident severity.
Meaning: The technical size of an incident does not always reflect its business impact.
5. Losing Evidence
Example: Follow approved collection and preservation procedures before making changes to affected systems.
Meaning: Evidence loss can make it harder to determine the root cause.
6. Communicating Unverified Details
Example: Clearly label estimates and unknowns in incident updates.
Meaning: Honest reporting builds trust and reduces confusion.
Improving Coordination and Recovery
7. Forgetting Third-Party Dependencies
Example: Assess whether a supplier or external service may be connected to the incident.
Meaning: Security issues can cross organizational boundaries.
8. Skipping Recovery Validation
Example: Verify security controls and system integrity before returning services to normal use.
Meaning: Recovery without validation may leave the original weakness unresolved.
9. Neglecting Staff Well-Being
Example: Plan reasonable shift handovers and backup coverage during prolonged incidents.
Meaning: Fatigue can affect judgment and response quality.
Maintaining Readiness and Learning From Incidents
10. Using Outdated Contact Lists
Example: Check incident contacts and escalation routes during scheduled plan reviews.
Meaning: Current details help notifications reach the correct people.
11. Closing Incidents Without Follow-Up
Example: Track unresolved corrective actions after the immediate threat is addressed.
Meaning: The incident may be closed operationally while important improvements remain necessary.
12. Blaming Instead of Learning
Example: Focus post-incident reviews on evidence, process gaps, and actionable improvements.
Meaning: A learning-focused review can strengthen future response without hiding accountability.
FAQs
What is an incident response team in cybersecurity?
It is a group that coordinates the detection, investigation, containment, and recovery of cybersecurity incidents.
What does an incident response team do?
It investigates threats, limits damage, preserves evidence, restores systems, and documents lessons learned.
What does CSIRT stand for?
CSIRT stands for Computer Security Incident Response Team.
Is a SOC the same as an incident response team?
Not exactly. A SOC monitors security activity, while incident responders focus on managing confirmed or suspected incidents.
Who should be on an incident response team?
Membership may include security analysts, IT specialists, forensic experts, legal advisers, and communications staff.
What skills does an incident response team need?
Useful skills include log analysis, threat investigation, containment, documentation, and clear communication.
Which framework helps guide incident response?
Organizations may use NIST guidance, ISO/IEC 27035, and internal playbooks suited to their needs.
Does every business need a dedicated response team?
Not necessarily. Smaller organizations may assign roles internally or use a qualified external provider.
How often should an incident response plan be tested?
Test it regularly and after major changes, incidents, or identified gaps in readiness.
What is the first step during a cyber incident?
Follow the response plan, report the event, assess immediate risks, and activate the appropriate response process.
Why is incident documentation important?
It preserves the timeline, supports decisions, improves accountability, and helps prevent repeat incidents.
How can an organization improve incident response?
Practice realistic scenarios, review incidents, update procedures, and complete corrective actions.
Conclusion
An effective incident response team cybersecurity program is about more than advanced software or a room full of monitoring screens. It brings together skilled people, clear responsibilities, reliable procedures, and thoughtful communication to manage security incidents from detection through recovery.
Whether you are building a response team, preparing for a cybersecurity career, or improving an existing program, start with defined roles, practical playbooks, tested recovery plans, and regular exercises. Every incident can reveal something useful when teams document their findings and turn lessons into action. Save this guide for your next security planning session, share it with your team, and keep strengthening your organization’s ability to respond with confidence.