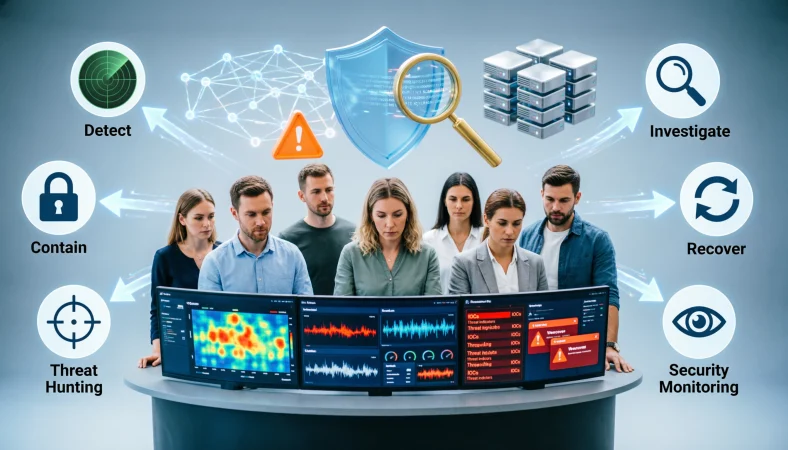
Attack detection and response is the process of spotting suspicious activity, investigating what happened, containing the threat, and taking steps to recover safely. Useful approaches include real-time monitoring, threat hunting, automated alerts, incident triage, and coordinated recovery.
Top alternatives: threat detection and response, cybersecurity attack detection, incident detection and response, security threat response, cyber attack monitoring
A suspicious login at midnight. A strange file suddenly appearing on a server. An endpoint connecting to an unfamiliar destination. These moments can turn an ordinary workday into a cybersecurity fire drill very quickly. Whether you are discussing security in a workplace, explaining an incident to a client, or researching cybersecurity terminology, attack detection and response describes the work of identifying potential attacks and taking appropriate action before the situation grows. Good security teams do not simply wait for alerts to appear.
They monitor activity, investigate unusual behavior, prioritize threats, contain incidents, and learn from what happened. The response also matters because spotting a threat is only half the job. A useful detection without a clear response can leave defenders scrambling. From endpoint monitoring and network visibility to threat intelligence and incident response plans, the right approach combines technology, people, and repeatable processes.
Funny Attack Detection and Response Ideas
“The firewall just raised an eyebrow.”
Example: Use this for a light internal security update about suspicious network activity.
Meaning: It humorously signals that something unusual deserves attention.
“Someone brought chaos to the login page.”
Example: Use this when discussing repeated failed authentication attempts.
Meaning: It makes an authentication alert sound memorable without minimizing the issue.
“The server saw something it did not like.”
Example: Use this for an informal explanation of an unusual server event.
Meaning: It indicates that system behavior triggered security concern.
“Alert level: definitely worth checking.”
Example: Use this when an alert looks unusual but still needs investigation.
Meaning: It communicates concern without immediately declaring a confirmed attack.
“The logs are telling a suspicious little story.”
Example: Use this when analysts notice several related events in logs.
Meaning: It suggests that separate clues may form a larger pattern.
“Someone knocked on the digital back door.”
Example: Use this when explaining suspicious access attempts to nontechnical colleagues.
Meaning: It describes an attempted unauthorized entry in simple language.
“The endpoint has entered detective mode.”
Example: Use this when endpoint monitoring begins investigating unusual behavior.
Meaning: It humorously describes increased security scrutiny.
“That login deserves a second look.”
Example: Use this after an unusual login location appears.
Meaning: It encourages investigation before making assumptions.
“The network is giving us side-eye.”
Example: Use this in a casual security team message about odd traffic.
Meaning: It signals that network behavior appears unusual.
“We found a digital plot twist.”
Example: Use this when an investigation reveals an unexpected connection between events.
Meaning: It highlights a surprising development during analysis.
“The alert inbox chose violence today.”
Example: Use this when a team receives an unusually high volume of alerts.
Meaning: It humorously describes a hectic monitoring period.
“Time to investigate before the plot thickens.”
Example: Use this when an early warning needs prompt review.
Meaning: It encourages timely investigation before suspicious activity escalates.
Professional Attack Detection and Response Strategies
“Validate the alert before escalating.”
Example: Use this when defining a first-level analyst workflow.
Meaning: It emphasizes confirming the signal before escalating an incident.
“Prioritize alerts by business impact.”
Example: Use this when creating an incident triage procedure.
Meaning: It directs teams to focus attention where consequences could be greatest.
“Document every significant response action.”
Example: Use this during incident response planning.
Meaning: It supports accountability and creates a useful investigation record.
“Separate detection from assumption.”
Example: Use this when training analysts to interpret alerts carefully.
Meaning: It reminds responders that an alert is evidence, not automatically proof of an attack.
“Correlate events across security layers.”
Example: Use this when investigating activity visible across endpoints and networks.
Meaning: It encourages analysts to combine multiple sources of evidence.
“Contain confirmed threats quickly.”
Example: Use this in a response policy focused on limiting damage.
Meaning: It emphasizes reducing an attacker’s ability to continue harmful activity.
“Preserve relevant evidence before remediation.”
Example: Use this when investigators need records for deeper analysis.
Meaning: It highlights the importance of retaining useful evidence before changing affected systems.
“Define escalation criteria in advance.”
Example: Use this when building an incident response procedure.
Meaning: It helps teams know when an event requires additional expertise or authority.
“Review detection coverage regularly.”
Example: Use this during a security program review.
Meaning: It encourages organizations to identify gaps in monitoring.
“Keep response ownership clear.”
Example: Use this when assigning incident responsibilities.
Meaning: It prevents uncertainty about who should take the next action.
“Test the response plan before an incident.”
Example: Use this during tabletop exercises.
Meaning: It helps reveal weaknesses before a real security event occurs.
“Turn every major incident into a lesson.”
Example: Use this during post-incident reviews.
Meaning: It encourages continuous improvement after security events.
Creative Attack Detection and Response Ideas
“Build a digital tripwire mindset.”
Example: Use this when explaining how security teams can identify meaningful warning signs.
Meaning: It encourages proactive thinking about indicators of compromise.
“Connect the dots, not just the alerts.”
Example: Use this when teaching analysts about event correlation.
Meaning: It focuses attention on relationships between individual security signals.
“Treat unusual behavior like a clue.”
Example: Use this when introducing behavioral detection concepts.
Meaning: It encourages investigation of deviations from expected activity.
“Give every alert a story.”
Example: Use this when analysts need to understand how events relate over time.
Meaning: It encourages building a timeline around suspicious activity.
“Make visibility your security superpower.”
Example: Use this in security awareness content about monitoring.
Meaning: It highlights the importance of knowing what is happening across an environment.
“Hunt for patterns hiding in plain sight.”
Example: Use this when discussing proactive threat hunting.
Meaning: It encourages searching for subtle relationships that automated alerts may miss.
“Think like the attacker, defend like the analyst.”
Example: Use this in threat hunting training.
Meaning: It encourages understanding likely attack behavior while maintaining a defensive perspective.
“Turn raw logs into useful clues.”
Example: Use this when explaining log analysis.
Meaning: It emphasizes extracting actionable information from security data.
“Let context make the alert smarter.”
Example: Use this when discussing alert enrichment.
Meaning: It shows why additional context can improve investigation quality.
“Design response paths before trouble arrives.”
Example: Use this when creating incident playbooks.
Meaning: It encourages preparation rather than improvisation.
“Build security stories from small signals.”
Example: Use this when discussing correlation across multiple events.
Meaning: It highlights how seemingly minor indicators can collectively become significant.
“Make every detection answer a question.”
Example: Use this when designing useful security alerts.
Meaning: It encourages alerts that help analysts understand what requires investigation.
Smart Attack Detection and Response Practices
“Detect first, investigate with context.”
Example: Use this when describing a balanced monitoring workflow.
Meaning: It combines rapid awareness with careful analysis.
“Prioritize signal over noise.”
Example: Use this when discussing alert fatigue.
Meaning: It emphasizes useful detections rather than overwhelming analysts with low-value alerts.
“Measure response time, not just alert volume.”
Example: Use this during security performance reviews.
Meaning: It focuses on how effectively teams act after detection.
“Know your normal before defining abnormal.”
Example: Use this when developing behavioral monitoring.
Meaning: It highlights the importance of establishing expected activity patterns.
“Correlate before concluding.”
Example: Use this when reviewing multiple suspicious events.
Meaning: It encourages evidence-based conclusions.
“Automate repetitive response steps carefully.”
Example: Use this when evaluating security automation.
Meaning: It supports automation while recognizing that some actions require human judgment.
“Keep high-risk actions under appropriate control.”
Example: Use this when designing automated containment.
Meaning: It encourages safeguards around disruptive response actions.
“Make detection rules measurable.”
Example: Use this when tuning security monitoring.
Meaning: It encourages teams to evaluate whether rules produce useful outcomes.
“Review false positives regularly.”
Example: Use this during detection engineering.
Meaning: It helps reduce unnecessary alerts and analyst fatigue.
“Connect technical alerts to business risk.”
Example: Use this when reporting incidents to leadership.
Meaning: It translates technical activity into practical organizational impact.
“Keep investigation timelines consistent.”
Example: Use this when standardizing analyst procedures.
Meaning: It makes investigations easier to review and compare.
“Use lessons learned to improve detection.”
Example: Use this after completing an incident review.
Meaning: It turns previous events into stronger future defenses.
Endpoint Attack Detection and Response
“Watch endpoints for unusual behavior.”
Example: Use this when explaining endpoint monitoring fundamentals.
Meaning: It focuses on identifying activity that differs from expected behavior.
“Investigate unexpected process activity.”
Example: Use this during endpoint threat hunting.
Meaning: It encourages analysts to review suspicious process execution.
“Monitor unusual account behavior.”
Example: Use this when discussing compromised credentials.
Meaning: It helps identify activity that may indicate unauthorized account use.
“Track suspicious file changes.”
Example: Use this when monitoring important systems.
Meaning: It highlights potentially meaningful modifications to files.
“Review unexpected persistence indicators.”
Example: Use this when investigating possible endpoint compromise.
Meaning: It focuses on signs that suspicious activity may survive system restarts.
“Isolate affected endpoints when appropriate.”
Example: Use this during containment planning.
Meaning: It describes a way to limit further communication or spread from a suspected system.
“Compare endpoint activity with known baselines.”
Example: Use this during behavioral analysis.
Meaning: It helps identify deviations from normal endpoint behavior.
“Keep endpoint telemetry useful and focused.”
Example: Use this during monitoring design.
Meaning: It encourages collecting information that supports meaningful investigation.
“Investigate suspicious parent-child processes.”
Example: Use this when analyzing unusual process relationships.
Meaning: It highlights a common source of investigative context.
“Review endpoint alerts alongside identity events.”
Example: Use this when investigating account-related endpoint activity.
Meaning: It combines host and identity evidence for stronger context.
“Preserve endpoint evidence during investigation.”
Example: Use this when handling a potentially compromised device.
Meaning: It emphasizes retaining useful evidence before making disruptive changes.
“Use endpoint findings to improve detections.”
Example: Use this after resolving a security incident.
Meaning: It turns endpoint investigation results into future monitoring improvements.
Network Attack Detection and Response
“Monitor traffic for unusual patterns.”
Example: Use this when explaining network detection basics.
Meaning: It focuses on identifying behavior outside expected network activity.
“Investigate unexpected outbound connections.”
Example: Use this when a system communicates with an unfamiliar destination.
Meaning: It encourages review of potentially suspicious external communication.
“Correlate network activity with endpoint events.”
Example: Use this during a broader investigation.
Meaning: It connects network evidence with activity on affected systems.
“Watch for unusual authentication traffic.”
Example: Use this when reviewing suspicious access patterns.
Meaning: It highlights network evidence that may support an identity investigation.
“Track changes in normal traffic volume.”
Example: Use this during anomaly monitoring.
Meaning: It helps identify significant deviations from expected network behavior.
“Investigate suspicious connection sequences.”
Example: Use this when multiple related network events appear.
Meaning: It encourages looking at event order rather than isolated alerts.
“Keep network telemetry searchable.”
Example: Use this when designing security monitoring infrastructure.
Meaning: It helps analysts investigate historical network activity efficiently.
“Use network context to enrich alerts.”
Example: Use this when improving detection quality.
Meaning: It adds useful communication details to security investigations.
“Identify critical network paths first.”
Example: Use this during monitoring prioritization.
Meaning: It focuses visibility on infrastructure where compromise could have greater consequences.
“Review unusual internal communication.”
Example: Use this when investigating possible lateral movement.
Meaning: It encourages analysis of unexpected system-to-system activity.
“Preserve relevant network records.”
Example: Use this during incident investigation planning.
Meaning: It supports later analysis of suspicious communications.
“Turn network findings into stronger rules.”
Example: Use this after an investigation reveals a recurring pattern.
Meaning: It encourages continuous improvement of network detection.
Sarcastic Attack Detection and Response Lines
“Because apparently the login needed an adventure.”
Example: Use this for an informal comment about an unusual authentication event.
Meaning: It lightly acknowledges suspicious activity without ignoring it.
“Nothing says Tuesday like a security alert.”
Example: Use this when an unexpected alert interrupts an ordinary workday.
Meaning: It uses humor to describe an inconvenient security event.
“The logs decided to become interesting.”
Example: Use this when routine logs reveal unusual activity.
Meaning: It signals that investigators have found something worth reviewing.
“Just what the alert queue ordered.”
Example: Use this when another investigation appears during a busy shift.
Meaning: It humorously describes an inconvenient addition to the workload.
“Our quiet network had other plans.”
Example: Use this when unexpected traffic appears.
Meaning: It points out that network behavior has changed.
“Someone clearly missed the security memo.”
Example: Use this when discussing suspicious activity in an informal setting.
Meaning: It humorously suggests that expected security behavior was not followed.
“The endpoint has entered its mysterious era.”
Example: Use this when a device behaves unusually.
Meaning: It humorously signals unexplained endpoint behavior.
“That alert is asking for attention.”
Example: Use this when a security notification looks significant.
Meaning: It encourages investigation without overstating certainty.
“The firewall is not feeling social today.”
Example: Use this when traffic is being blocked or scrutinized.
Meaning: It humorously describes restrictive network behavior.
“The credentials chose an interesting location.”
Example: Use this when authentication occurs from an unusual place.
Meaning: It points toward a potentially suspicious login.
“The timeline has entered detective territory.”
Example: Use this when investigators begin correlating events.
Meaning: It signals that deeper analysis is needed.
“Another day, another suspicious timestamp.”
Example: Use this during informal security team commentary.
Meaning: It humorously describes recurring investigation clues.
Clear and Simple Attack Detection and Response Explanations
“Spot the threat, then understand it.”
Example: Use this when explaining detection and investigation to beginners.
Meaning: It separates initial discovery from deeper analysis.
“Find unusual activity before it becomes bigger.”
Example: Use this in basic cybersecurity education.
Meaning: It explains the preventive value of early detection.
“Detect, investigate, contain, recover.”
Example: Use this when summarizing a response lifecycle.
Meaning: It gives a simple framework for handling security incidents.
“An alert is a starting point.”
Example: Use this when explaining why alerts need investigation.
Meaning: It reminds readers that alerts require context.
“Good response starts with good visibility.”
Example: Use this when explaining monitoring fundamentals.
Meaning: It highlights the importance of knowing what is happening in an environment.
“Not every alert means an attack.”
Example: Use this when teaching alert triage.
Meaning: It emphasizes careful validation.
“Not every attack looks obvious.”
Example: Use this during security awareness training.
Meaning: It highlights why behavioral clues and context matter.
“Context turns data into evidence.”
Example: Use this when explaining security analytics.
Meaning: It shows why isolated events are less useful than connected information.
“Response should match the risk.”
Example: Use this when explaining incident prioritization.
Meaning: It encourages proportionate response decisions.
“Containment limits the attacker’s room to move.”
Example: Use this when introducing containment concepts.
Meaning: It explains the purpose of limiting compromised activity.
“Recovery is part of the response.”
Example: Use this when discussing incident lifecycle planning.
Meaning: It reminds readers that restoring normal operations matters too.
“Every incident can improve the next detection.”
Example: Use this during post-incident discussions.
Meaning: It emphasizes continuous learning.
Confident Attack Detection and Response Statements
“We investigate signals, not assumptions.”
Example: Use this in a security team statement about analytical discipline.
Meaning: It communicates confidence in evidence-based investigation.
“Visibility gives defenders options.”
Example: Use this when discussing monitoring capabilities.
Meaning: It emphasizes how information supports better response choices.
“We prepare before the alert arrives.”
Example: Use this in incident readiness documentation.
Meaning: It highlights proactive preparation.
“Every critical alert has an owner.”
Example: Use this when defining operational responsibilities.
Meaning: It establishes accountability for response actions.
“Containment starts with knowing what matters.”
Example: Use this when prioritizing incident response.
Meaning: It connects effective containment with asset and business awareness.
“Detection without action is unfinished work.”
Example: Use this when explaining the relationship between detection and response.
Meaning: It emphasizes that identification should lead to appropriate action.
“We investigate the signal and verify the story.”
Example: Use this when describing an analyst mindset.
Meaning: It combines alert review with evidence gathering.
“Security decisions need useful evidence.”
Example: Use this during incident response training.
Meaning: It emphasizes evidence-based decision-making.
“Prepared teams respond with less confusion.”
Example: Use this when discussing incident playbooks.
Meaning: It highlights the value of preparation.
“Strong response begins before impact spreads.”
Example: Use this when explaining early containment.
Meaning: It emphasizes timely action to limit consequences.
“Clear roles make urgent work manageable.”
Example: Use this during response planning.
Meaning: It shows why defined responsibilities matter during incidents.
“Better detections create better decisions.”
Example: Use this when discussing detection engineering.
Meaning: It connects detection quality with response quality.
Chill and Casual Attack Detection and Response Ideas
“Let’s check what’s actually happening.”
Example: Use this when an alert needs calm investigation.
Meaning: It encourages analysis without unnecessary panic.
“Worth a quick look.”
Example: Use this for a low-context alert that still deserves review.
Meaning: It signals moderate investigative priority.
“Let’s connect the dots.”
Example: Use this when several alerts may be related.
Meaning: It encourages correlation.
“First, context. Then conclusions.”
Example: Use this when reminding analysts to avoid assumptions.
Meaning: It promotes evidence-based investigation.
“Let’s see what the logs say.”
Example: Use this when beginning an investigation.
Meaning: It points toward available evidence.
“Something looks a little off.”
Example: Use this when activity deviates from normal behavior.
Meaning: It expresses concern without overclaiming.
“Let’s keep an eye on it.”
Example: Use this when monitoring an event that does not yet require escalation.
Meaning: It suggests continued observation.
“Check first, panic never.”
Example: Use this in casual security awareness content.
Meaning: It encourages calm investigation.
“Let’s follow the evidence.”
Example: Use this during collaborative analysis.
Meaning: It encourages decisions based on available facts.
“That pattern deserves attention.”
Example: Use this when multiple events appear connected.
Meaning: It signals that further review is justified.
“Let’s figure out the timeline.”
Example: Use this when reconstructing an incident.
Meaning: It focuses on understanding event sequence.
“One clue at a time.”
Example: Use this during a complex investigation.
Meaning: It encourages systematic analysis.
Emotional Attack Detection and Response Perspectives
“Security is about protecting people, not just systems.”
Example: Use this in awareness content focused on human impact.
Meaning: It connects cybersecurity with people and organizational trust.
“Every alert can protect something important.”
Example: Use this when motivating security teams.
Meaning: It highlights the real-world value of timely detection.
“Behind every incident is a business that needs answers.”
Example: Use this during incident response training.
Meaning: It emphasizes the importance of clear communication.
“Preparedness reduces uncertainty when pressure rises.”
Example: Use this when discussing response planning.
Meaning: It highlights the human benefit of preparation.
“Good security gives teams confidence.”
Example: Use this when describing effective detection programs.
Meaning: It connects visibility with operational confidence.
“Every investigation deserves patience and precision.”
Example: Use this when discussing analyst responsibilities.
Meaning: It balances urgency with careful reasoning.
“A calm response can change the whole incident.”
Example: Use this during security awareness training.
Meaning: It highlights the value of controlled decision-making.
“Protect the evidence and protect the story.”
Example: Use this when explaining evidence preservation.
Meaning: It stresses maintaining trustworthy investigative information.
“Learning after an incident matters.”
Example: Use this during post-incident review guidance.
Meaning: It emphasizes improvement rather than simply closing the ticket.
“Security teams carry more than alerts.”
Example: Use this in content about incident response responsibilities.
Meaning: It recognizes the broader organizational impact of security work.
“Every response should move toward stability.”
Example: Use this when describing recovery goals.
Meaning: It frames response as a path back to safe operations.
“The best lesson is the one you actually use.”
Example: Use this after a security incident review.
Meaning: It encourages turning lessons learned into practical improvements.
Clever Attack Detection and Response Concepts
“Context is the missing puzzle piece.”
Example: Use this when explaining alert enrichment.
Meaning: It shows how additional information can make a detection more useful.
“A single signal can become a pattern.”
Example: Use this when introducing correlation.
Meaning: It explains how repeated or connected events can reveal larger activity.
“Baseline first, anomaly second.”
Example: Use this during behavioral detection planning.
Meaning: It emphasizes understanding normal activity before identifying deviations.
“Detection is observation with a purpose.”
Example: Use this when defining security monitoring.
Meaning: It frames detection as purposeful identification rather than passive data collection.
“Response is detection put into motion.”
Example: Use this when explaining the relationship between monitoring and action.
Meaning: It connects identification with appropriate operational response.
“Good telemetry shortens the investigation.”
Example: Use this when discussing security data collection.
Meaning: It highlights how useful information can improve investigation efficiency.
“The timeline often tells the real story.”
Example: Use this when investigating multiple events.
Meaning: It emphasizes event sequence as an important analytical tool.
“Risk gives the alert its priority.”
Example: Use this during incident triage discussions.
Meaning: It connects alert importance with potential consequences.
“Automation handles repetition; analysts handle judgment.”
Example: Use this when discussing security automation.
Meaning: It describes a balanced approach to automated and human decision-making.
“Every detection rule makes a claim.”
Example: Use this when discussing detection engineering.
Meaning: It reminds teams that rules should be tested against expected behavior.
“False positives teach you where the rule needs work.”
Example: Use this during detection tuning.
Meaning: It frames false positives as useful feedback for improvement.
“The strongest response starts with the clearest question.”
Example: Use this when beginning an investigation.
Meaning: It encourages focused investigative thinking.
Threat Hunting Attack Detection and Response Ideas
“Hunt beyond the obvious alerts.”
Example: Use this when introducing proactive threat hunting.
Meaning: It encourages searching for activity that automated systems may not flag.
“Start with a meaningful hypothesis.”
Example: Use this when planning a hunting exercise.
Meaning: It gives the investigation a focused starting point.
“Search for behavior, not just signatures.”
Example: Use this when discussing behavioral threat hunting.
Meaning: It emphasizes patterns that may reveal previously unknown activity.
“Follow unusual authentication patterns.”
Example: Use this during identity-focused threat hunting.
Meaning: It encourages analysis of unexpected account behavior.
“Look for activity that breaks the baseline.”
Example: Use this during anomaly-focused hunting.
Meaning: It directs attention toward meaningful deviations.
“Hunt across multiple data sources.”
Example: Use this when planning a broad investigation.
Meaning: It encourages combining endpoint, identity, network, and other telemetry.
“Document what the hunt proves and disproves.”
Example: Use this during threat hunting exercises.
Meaning: It creates a clearer record of investigative conclusions.
“Turn successful hunts into detections.”
Example: Use this after discovering a repeatable suspicious pattern.
Meaning: It converts proactive findings into ongoing monitoring capability.
“Review old incidents for new clues.”
Example: Use this during retrospective threat hunting.
Meaning: It encourages reexamining historical evidence.
“Hunt where visibility is strongest first.”
Example: Use this when prioritizing investigative areas.
Meaning: It makes efficient use of available telemetry.
“Use intelligence to shape hunting questions.”
Example: Use this when incorporating threat intelligence.
Meaning: It connects external knowledge with focused defensive investigation.
“Make hunting a learning loop.”
Example: Use this when building a recurring hunting program.
Meaning: It encourages findings to improve detections and future investigations.
Automated Attack Detection and Response Ideas
“Automate the repetitive, not the uncertain.”
Example: Use this when designing security automation.
Meaning: It suggests automating predictable tasks while preserving human judgment for ambiguous cases.
“Let automation enrich alerts.”
Example: Use this when improving analyst workflows.
Meaning: It encourages automatic addition of useful context.
“Use automation to reduce response delays.”
Example: Use this when discussing security orchestration.
Meaning: It highlights automation’s ability to speed appropriate actions.
“Create approval steps for disruptive actions.”
Example: Use this when designing automated containment.
Meaning: It adds safeguards around actions that could affect business operations.
“Automate evidence collection where appropriate.”
Example: Use this during response workflow design.
Meaning: It can reduce repetitive investigative work.
“Use automated prioritization carefully.”
Example: Use this when discussing alert ranking systems.
Meaning: It recognizes that automated prioritization should be validated.
“Make automated actions visible to responders.”
Example: Use this when implementing response automation.
Meaning: It keeps human responders informed about system actions.
“Test automation before relying on it.”
Example: Use this during security workflow implementation.
Meaning: It emphasizes validation before operational dependence.
“Build safe failure paths.”
Example: Use this when designing automated response procedures.
Meaning: It prepares the system for situations where automation cannot confidently act.
“Use automation to improve consistency.”
Example: Use this when standardizing repetitive response tasks.
Meaning: It highlights consistency as a benefit of controlled automation.
“Review automated actions after incidents.”
Example: Use this during post-incident analysis.
Meaning: It helps teams identify automation improvements.
“Keep humans in the loop where risk demands it.”
Example: Use this when discussing high-impact automated decisions.
Meaning: It balances speed with appropriate oversight.
Best Practices for Attack Detection and Response
“Know what you need to protect.”
Example: Use this when beginning a security monitoring program.
Meaning: It establishes asset awareness as a foundation for detection.
“Define normal behavior.”
Example: Use this when creating behavioral detection rules.
Meaning: It provides a baseline for identifying anomalies.
“Centralize useful security visibility.”
Example: Use this when improving monitoring architecture.
Meaning: It makes relevant information easier to investigate.
“Tune detections regularly.”
Example: Use this during ongoing security operations.
Meaning: It helps maintain useful alert quality as environments change.
“Prioritize incidents consistently.”
Example: Use this when establishing triage procedures.
Meaning: It creates a repeatable approach to deciding which events need urgent attention.
“Keep response roles documented.”
Example: Use this when maintaining an incident response plan.
Meaning: It clarifies responsibilities during security events.
“Protect and preserve investigation evidence.”
Example: Use this when defining incident handling procedures.
Meaning: It supports reliable investigation and review.
“Exercise response procedures.”
Example: Use this when preparing teams for real incidents.
Meaning: It helps uncover weaknesses before they matter operationally.
“Review incidents after containment.”
Example: Use this after resolving a security event.
Meaning: It ensures the organization learns from what happened.
“Improve detections from real findings.”
Example: Use this during continuous security improvement.
Meaning: It turns incident experience into stronger monitoring.
“Measure meaningful response outcomes.”
Example: Use this during security program reviews.
Meaning: It focuses performance measurement on useful operational results.
“Keep improving as the environment changes.”
Example: Use this during long-term security planning.
Meaning: It recognizes that effective detection and response must evolve with technology and threats.
FAQs
What does attack detection and response mean?
Attack detection and response refers to identifying suspicious or malicious activity, investigating the evidence, containing appropriate threats, and supporting recovery and improvement.
What is the difference between attack detection and response?
Detection focuses on recognizing potentially harmful activity, while response focuses on investigating, containing, resolving, and learning from the incident.
What does attack detection and response include?
It can include monitoring, alerting, threat hunting, investigation, incident triage, containment, evidence preservation, recovery, and post-incident improvement.
Can attack detection and response be automated?
Yes. Certain repetitive tasks such as alert enrichment, notification, evidence collection, and predefined response actions can be automated, while higher-risk decisions may require human oversight.
Is attack detection and response only for large organizations?
No. Organizations of different sizes can use detection and response practices. The technologies, staffing, processes, and level of automation can vary according to the environment and risk.
Why is attack detection important?
Early detection can give defenders more time to investigate suspicious activity and take appropriate action before an incident creates broader consequences.
Why does response matter after detecting an attack?
Detection identifies a potential problem, but response determines what happens next. A structured response can help contain the situation, support investigation, restore operations, and improve future defenses.
What should you say if you do not actually mean an alert is an attack?
Use precise language such as “This activity requires investigation” or “This alert has not yet been confirmed as malicious.” Clear wording prevents assumptions from becoming conclusions.
Is humor appropriate when discussing attack detection and response?
Light humor can work in informal training or team communication, but actual incident procedures, alerts, and executive communications should remain clear, precise, and appropriately serious.
Can attack detection and response help reduce alert fatigue?
Yes. Detection tuning, prioritization, correlation, contextual enrichment, and controlled automation can help teams focus attention on more meaningful alerts.
What makes an attack detection and response process effective?
Useful visibility, clear responsibilities, appropriate alert prioritization, repeatable response procedures, evidence preservation, regular testing, and continuous improvement all contribute to a stronger process.
How can teams improve attack detection and response over time?
Teams can review incidents, tune detection rules, test response procedures, improve telemetry, analyze false positives, update playbooks, and convert useful investigation findings into better detections.
Conclusion
Good attack detection and response is not about reacting dramatically to every notification. It is about noticing meaningful signals, understanding what they mean, responding appropriately, and learning from every investigation. The best responses feel organized even when the situation is anything but organized. Whether you are building security procedures, explaining cybersecurity to a team, or simply learning the terminology, the right wording can make complicated concepts much easier to understand.
Try different approaches based on the audience, situation, and level of urgency. Save this list for your next security discussion, share it with someone working on incident response, and reuse the ideas whenever you need a clearer way to explain detection and response.