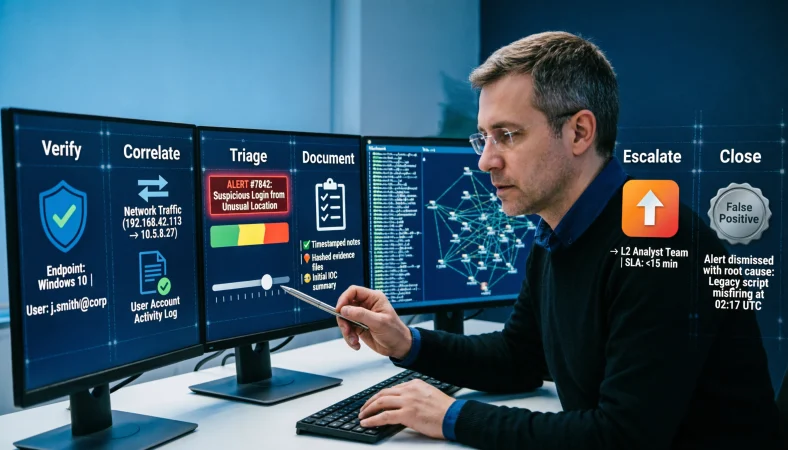
A false positive first response is the initial process of checking whether a security alert represents a real incident or harmless activity before escalating unnecessarily. A practical first response typically includes verification, triage, documentation, correlation, and appropriate escalation.
Top alternatives: false positive response, first response to a false positive, false positive alert handling, security alert verification, incident alert triage
One security alert can turn a normal workday into instant detective mode. Then comes the plot twist: it may not even be a real incident. That is where false positive first response practices become useful. In cybersecurity, analysts often need to determine whether an alert represents genuine malicious activity or legitimate behavior before committing major response resources.
A sensible first response can involve validating the alert, checking relevant logs, correlating evidence, documenting findings, and deciding whether escalation is justified. This matters in a SOC, IT help desk, incident response team, or security operations workflow because unnecessary containment can disrupt legitimate business activity, while dismissing a genuine alert can create an entirely different problem.
The goal is simple: slow down enough to verify the signal, but not so much that a real threat gets comfortable.
False Positive First Response Basics
“Verify before you escalate.”
Example: Use this when an alert appears suspicious but lacks supporting evidence.
Meaning: Confirm the signal before treating it as a confirmed incident.
“Start with the alert itself.”
Example: Use this when beginning an investigation from a new SIEM notification.
Meaning: Review what actually triggered the detection.
“Check the surrounding context.”
Example: Use this when an alert could be explained by normal user activity.
Meaning: Context helps separate suspicious behavior from legitimate activity.
“Do not assume every alert is an incident.”
Example: Use this when training junior analysts.
Meaning: An alert requires analysis before incident classification.
“Correlate before concluding.”
Example: Use this when several security logs are available.
Meaning: Multiple evidence sources can provide stronger context.
“Document what you find.”
Example: Use this during every alert investigation.
Meaning: Recording evidence makes the decision traceable.
“Check whether the activity was expected.”
Example: Use this when investigating administrative activity.
Meaning: Authorized behavior can sometimes trigger security detections.
“Confirm the affected asset.”
Example: Use this when an alert references an unfamiliar endpoint.
Meaning: Identifying the correct asset prevents investigation errors.
“Identify the triggering event.”
Example: Use this when an alert contains multiple related events.
Meaning: Understanding the trigger clarifies what needs verification.
“Separate signal from noise.”
Example: Use this when an analyst faces a crowded alert queue.
Meaning: The objective is to identify meaningful security evidence.
“Use evidence, not assumptions.”
Example: Use this when an alert appears urgent but incomplete.
Meaning: Decisions should rely on available facts.
“Record the final disposition.”
Example: Use this when closing an alert as benign.
Meaning: The outcome should be documented for future reference.
A first response process commonly begins by confirming whether a reported event is a false positive and establishing basic incident details before moving further into response.
False Positive First Response For SOC Analysts
“Read the alert details first.”
Example: Use this when a SOC analyst receives a high-volume detection.
Meaning: The alert provides the starting evidence for triage.
“Check the detection rule.”
Example: Use this when the same alert repeatedly fires on normal activity.
Meaning: Rule logic may explain recurring false positives.
“Review recent activity.”
Example: Use this when investigating an unusual login alert.
Meaning: Nearby events can reveal whether the activity was expected.
“Compare multiple data sources.”
Example: Use this when one security product produces an unusual alert.
Meaning: Correlation can strengthen or weaken the initial finding.
“Check the user context.”
Example: Use this when an alert involves a privileged account.
Meaning: Role and normal behavior can change the interpretation.
“Check the asset context.”
Example: Use this when investigating endpoint activity.
Meaning: Device purpose and ownership can explain unusual behavior.
“Review known maintenance activity.”
Example: Use this when alerts appear during a scheduled change.
Meaning: Planned work can produce legitimate security signals.
“Look for related indicators.”
Example: Use this when a single alert seems incomplete.
Meaning: Additional indicators can help confirm or dismiss the suspicion.
“Assign a clear disposition.”
Example: Use this when completing initial triage.
Meaning: The alert should have an understandable outcome.
“Escalate uncertainty when appropriate.”
Example: Use this when evidence remains inconclusive.
Meaning: Analysts should not force a benign conclusion without enough evidence.
“Keep the investigation reproducible.”
Example: Use this when documenting analyst actions.
Meaning: Another analyst should be able to understand what happened.
“Close the loop with detection engineering.”
Example: Use this when a rule repeatedly creates harmless alerts.
Meaning: Recurring false positives may justify detection improvements.
False Positive First Response Steps
“Receive the alert.”
Example: Use this when documenting the beginning of an alert workflow.
Meaning: The response starts when a detection enters the queue.
“Validate the trigger.”
Example: Use this when the alert contains incomplete information.
Meaning: Confirm that the underlying event actually occurred.
“Identify the affected entity.”
Example: Use this when investigating a user, endpoint, IP, or application.
Meaning: Establish what the alert concerns.
“Review supporting evidence.”
Example: Use this when determining whether the alert has credibility.
Meaning: Evidence helps establish whether the signal is meaningful.
“Correlate related events.”
Example: Use this when several logs cover the same timeframe.
Meaning: Related events can reveal a larger pattern.
“Check legitimate explanations.”
Example: Use this when an alert may result from normal operations.
Meaning: Authorized activity should be considered during triage.
“Assess potential impact.”
Example: Use this when suspicious activity cannot yet be dismissed.
Meaning: Analysts should understand what could be affected.
“Determine confidence.”
Example: Use this when evidence is mixed.
Meaning: Confidence helps guide escalation decisions.
“Document the analysis.”
Example: Use this when closing or escalating an alert.
Meaning: The reasoning should remain visible.
“Escalate when evidence supports it.”
Example: Use this when indicators point toward genuine malicious activity.
Meaning: Confirmed risk should receive appropriate attention.
“Close verified false positives.”
Example: Use this when investigation shows legitimate activity.
Meaning: The alert can be resolved without unnecessary incident escalation.
“Feed lessons back into the process.”
Example: Use this when recurring false positives are identified.
Meaning: Previous investigations can improve future detection and triage.
False Positive First Response In Incident Triage
“Triage before containment.”
Example: Use this when an alert has not yet been validated.
Meaning: Initial analysis helps determine whether containment is justified.
“Confirm the incident scope.”
Example: Use this when several assets appear in related alerts.
Meaning: Scope prevents responders from investigating blindly.
“Check whether the alert is isolated.”
Example: Use this when only one endpoint appears suspicious.
Meaning: A single event may have a different interpretation from a broader pattern.
“Look for corroborating indicators.”
Example: Use this when deciding whether escalation is warranted.
Meaning: Independent evidence can increase confidence.
“Review timestamps carefully.”
Example: Use this when correlating authentication and endpoint events.
Meaning: Timing can reveal whether events are actually related.
“Check asset ownership.”
Example: Use this when an unfamiliar system appears in an alert.
Meaning: Ownership can explain authorized activity.
“Check user authorization.”
Example: Use this when privileged behavior triggers detection.
Meaning: Authorized administrative actions may be legitimate.
“Consider recent changes.”
Example: Use this when an alert appears after a deployment.
Meaning: System changes can produce unexpected but legitimate activity.
“Keep severity evidence-based.”
Example: Use this when assigning an initial priority.
Meaning: Severity should reflect available evidence and potential impact.
“Do not bury uncertain alerts.”
Example: Use this when evidence remains ambiguous.
Meaning: Uncertainty should be visible rather than hidden.
“Escalate genuine risk promptly.”
Example: Use this when multiple indicators support compromise.
Meaning: Confirmed concerns should move into the appropriate response path.
“Close only with documented reasoning.”
Example: Use this when marking an alert as benign.
Meaning: The disposition should be explainable later.
False Positive First Response In SIEM
“Inspect the raw event.”
Example: Use this when a SIEM alert seems misleading.
Meaning: Raw data can reveal details hidden by the summary.
“Review the detection query.”
Example: Use this when a rule repeatedly fires incorrectly.
Meaning: Query logic can reveal why benign activity is being selected.
“Check event normalization.”
Example: Use this when different data sources appear inconsistent.
Meaning: Parsing issues can affect alert accuracy.
“Compare adjacent events.”
Example: Use this when an alert lacks sufficient context.
Meaning: Nearby events may explain the trigger.
“Search the same indicator.”
Example: Use this when an IP, user, or hostname appears suspicious.
Meaning: Historical occurrences can add context.
“Review historical behavior.”
Example: Use this when an alert concerns a normally active account.
Meaning: Baselines can help identify unusual changes.
“Check the alert frequency.”
Example: Use this when the same detection fires repeatedly.
Meaning: Frequency can reveal systematic false positives.
“Look for related detections.”
Example: Use this when one alert may be part of a larger pattern.
Meaning: Correlated detections can increase confidence.
“Preserve useful evidence.”
Example: Use this when an alert might later require escalation.
Meaning: Important data should remain available for analysis.
“Document the SIEM disposition.”
Example: Use this when resolving an alert.
Meaning: The final status should be recorded.
“Tune carefully.”
Example: Use this when adjusting an overly noisy detection.
Meaning: Reducing noise should not unnecessarily remove useful coverage.
“Retest after tuning.”
Example: Use this after changing a detection rule.
Meaning: Rule changes should be checked against expected and suspicious activity.
False Positive First Response In EDR
“Identify the endpoint.”
Example: Use this when an EDR alert references multiple devices.
Meaning: The investigation needs a clearly identified host.
“Review the process tree.”
Example: Use this when suspicious execution is detected.
Meaning: Parent and child processes can provide valuable context.
“Check the initiating user.”
Example: Use this when endpoint activity involves an account.
Meaning: User identity can help explain whether activity is authorized.
“Review command-line details.”
Example: Use this when an execution alert looks unusual.
Meaning: Command context may distinguish legitimate administration from suspicious behavior.
“Check recent software changes.”
Example: Use this when an alert follows a deployment.
Meaning: New software can explain unfamiliar endpoint behavior.
“Look for persistence indicators.”
Example: Use this when the alert involves unusual execution.
Meaning: Persistence evidence can increase the significance of the event.
“Check network connections.”
Example: Use this when endpoint activity includes outbound communication.
Meaning: Network context can help clarify suspicious behavior.
“Review file reputation carefully.”
Example: Use this when a newly detected file triggers an alert.
Meaning: Reputation information can support but should not replace contextual analysis.
“Compare with known-good behavior.”
Example: Use this when activity appears unusual.
Meaning: Baselines help identify deviations.
“Avoid unnecessary isolation.”
Example: Use this when evidence points toward legitimate activity.
Meaning: Containment can disrupt business operations when the alert is benign.
“Document the endpoint findings.”
Example: Use this when resolving an EDR alert.
Meaning: Findings should remain available for future review.
“Feed recurring patterns back to detection teams.”
Example: Use this when legitimate endpoint activity repeatedly triggers alerts.
Meaning: Detection improvements can reduce future investigation noise.
False Positive First Response In Network Security
“Verify the source address.”
Example: Use this when an alert identifies suspicious network traffic.
Meaning: Confirming the source helps avoid investigating the wrong system.
“Check the destination.”
Example: Use this when outbound communication triggers an alert.
Meaning: Destination context can clarify the activity.
“Review traffic timing.”
Example: Use this when unusual traffic appears during scheduled maintenance.
Meaning: Timing may provide a legitimate explanation.
“Correlate firewall logs.”
Example: Use this when network telemetry appears incomplete.
Meaning: Additional network data can strengthen analysis.
“Check DNS activity.”
Example: Use this when investigating suspicious domain communication.
Meaning: DNS context can help explain network behavior.
“Review authentication events.”
Example: Use this when network activity involves a specific account.
Meaning: Authentication records can add identity context.
“Check expected service behavior.”
Example: Use this when an application generates unusual connections.
Meaning: Normal application behavior can resemble suspicious activity.
“Look for repeated patterns.”
Example: Use this when a network alert appears more than once.
Meaning: Repetition may reveal either routine activity or a broader issue.
“Avoid blocking without verification.”
Example: Use this when a suspicious address may belong to a legitimate service.
Meaning: Premature blocking can interrupt valid business traffic.
“Document network evidence.”
Example: Use this when completing network alert triage.
Meaning: Recorded evidence supports later review.
“Escalate confirmed malicious activity.”
Example: Use this when multiple network indicators align.
Meaning: Corroborated threats require appropriate response.
“Review noisy network rules.”
Example: Use this when analysts repeatedly dismiss the same detection.
Meaning: Persistent noise may indicate a rule-quality problem.
False Positive First Response Documentation
“Record the alert source.”
Example: Use this when opening an investigation ticket.
Meaning: The origin of the signal should be clear.
“Record the detection time.”
Example: Use this when documenting the alert timeline.
Meaning: Timing helps correlate other evidence.
“Record the affected asset.”
Example: Use this when documenting an endpoint investigation.
Meaning: The system involved should be identifiable.
“Record the user involved.”
Example: Use this when an account appears in the alert.
Meaning: User context can support later analysis.
“Record the evidence reviewed.”
Example: Use this when closing a false positive.
Meaning: The decision should show what was actually checked.
“Record relevant logs.”
Example: Use this when several telemetry sources were consulted.
Meaning: Important evidence should remain traceable.
“Record the analyst decision.”
Example: Use this when finalizing triage.
Meaning: The disposition should be explicit.
“Record uncertainty.”
Example: Use this when evidence is incomplete.
Meaning: Unknowns should not be disguised as certainty.
“Record escalation details.”
Example: Use this when transferring a case to another team.
Meaning: The next responder needs useful context.
“Record rule-related observations.”
Example: Use this when the alert appears systematically noisy.
Meaning: Detection issues can be addressed later.
“Use consistent terminology.”
Example: Use this when several analysts share the same queue.
Meaning: Consistent language makes cases easier to understand.
“Keep the final disposition searchable.”
Example: Use this when closing large volumes of alerts.
Meaning: Historical decisions can help future investigations.
False Positive First Response For Security Alerts
“Pause and verify.”
Example: Use this when a high-priority alert arrives without context.
Meaning: Verification should precede unnecessary escalation.
“Check whether the activity is expected.”
Example: Use this when a user performs unusual administrative actions.
Meaning: Legitimate work can resemble suspicious behavior.
“Review the alert confidence.”
Example: Use this when detection metadata provides a confidence indicator.
Meaning: Confidence can help guide further analysis.
“Look for supporting indicators.”
Example: Use this when a single alert appears weak.
Meaning: Additional evidence can strengthen or weaken the case.
“Check recent changes.”
Example: Use this when an alert follows system maintenance.
Meaning: Recent changes may explain unusual behavior.
“Review historical activity.”
Example: Use this when determining whether the behavior is normal.
Meaning: Previous activity can provide a useful baseline.
“Identify business context.”
Example: Use this when security activity occurs during a major project.
Meaning: Business operations can explain otherwise unusual events.
“Do not suppress blindly.”
Example: Use this when analysts repeatedly see the same alert.
Meaning: Reducing noise should not eliminate meaningful detection.
“Escalate when evidence accumulates.”
Example: Use this when multiple indicators begin pointing toward compromise.
Meaning: Increasing evidence can justify moving beyond basic triage.
“Close with a reason.”
Example: Use this when resolving a benign alert.
Meaning: The decision should be understandable later.
“Review recurring false positives.”
Example: Use this during weekly SOC process reviews.
Meaning: Repeated noise can reveal detection weaknesses.
“Turn lessons into improvements.”
Example: Use this when a recurring alert pattern is identified.
Meaning: Past triage should help improve future detection.
False Positive First Response And Escalation
“Escalate evidence, not anxiety.”
Example: Use this when an alert initially looks frightening.
Meaning: Escalation should be based on meaningful indicators.
“Know the escalation criteria.”
Example: Use this when training new SOC analysts.
Meaning: Clear criteria make escalation more consistent.
“Escalate unresolved uncertainty when necessary.”
Example: Use this when the analyst cannot confidently dismiss the alert.
Meaning: Uncertainty can justify additional expertise.
“Provide context with every escalation.”
Example: Use this when transferring an investigation.
Meaning: The receiving team needs more than the alert title.
“Include evidence reviewed.”
Example: Use this when escalating a suspicious event.
Meaning: Evidence helps the next analyst continue efficiently.
“Include affected assets.”
Example: Use this when escalating a possible compromise.
Meaning: Asset details help establish scope.
“Include the current assessment.”
Example: Use this when handing over a case.
Meaning: The next responder should understand the current conclusion.
“Separate confirmed facts from assumptions.”
Example: Use this when documenting an uncertain case.
Meaning: Clear distinction prevents misunderstanding.
“Do not overstate severity.”
Example: Use this when escalating a suspicious but incomplete alert.
Meaning: Accurate classification supports better decision-making.
“Do not understate credible risk.”
Example: Use this when multiple indicators support malicious activity.
Meaning: Genuine concerns should receive appropriate attention.
“Use the documented escalation path.”
Example: Use this when a case meets incident criteria.
Meaning: Established procedures reduce confusion.
“Update the case after escalation.”
Example: Use this when new evidence appears.
Meaning: Escalation does not end documentation.
False Positive First Response For Automated Detection
“Automation should trigger analysis, not blind action.”
Example: Use this when designing automated security workflows.
Meaning: Automated alerts still need appropriate validation.
“Validate automated alerts.”
Example: Use this when an automated system produces a suspicious event.
Meaning: Automation can identify candidates without proving malicious intent.
“Use safe automation.”
Example: Use this when considering automatic containment.
Meaning: Automated actions should account for the consequences of mistakes.
“Create clear exception rules.”
Example: Use this when known legitimate activity repeatedly triggers alerts.
Meaning: Well-defined exceptions can reduce unnecessary noise.
“Monitor automated decisions.”
Example: Use this when deploying automated alert handling.
Meaning: Automation should remain observable.
“Review automation failures.”
Example: Use this when a system repeatedly misclassifies activity.
Meaning: Errors can reveal weaknesses in the workflow.
“Keep humans involved where impact is high.”
Example: Use this when automation could disrupt critical systems.
Meaning: Significant actions may require human judgment.
“Log automated actions.”
Example: Use this when configuring automated response systems.
Meaning: Every automated action should remain traceable.
“Test before broad deployment.”
Example: Use this when introducing a new response workflow.
Meaning: Testing helps reveal unexpected outcomes.
“Measure false positive patterns.”
Example: Use this when reviewing automated detection quality.
Meaning: Trends reveal where automation needs improvement.
“Review exception lists regularly.”
Example: Use this when managing known-safe entities.
Meaning: Old exceptions can become inaccurate over time.
“Keep automation aligned with current risk.”
Example: Use this during periodic security reviews.
Meaning: Automated response should reflect the current environment.
False Positive First Response And Detection Tuning
“Find the source of the noise.”
Example: Use this when one detection creates hundreds of alerts.
Meaning: The underlying rule or behavior should be investigated.
“Review detection thresholds.”
Example: Use this when legitimate activity crosses a trigger threshold.
Meaning: Thresholds can influence alert volume.
“Check the baseline.”
Example: Use this when normal behavior is repeatedly flagged.
Meaning: Baseline knowledge can improve detection accuracy.
“Compare true and false alerts.”
Example: Use this when evaluating a detection rule.
Meaning: Contrasting examples can reveal useful tuning opportunities.
“Avoid over-tuning.”
Example: Use this when reducing a noisy detection.
Meaning: Excessive suppression can weaken security visibility.
“Test rule changes.”
Example: Use this after modifying detection logic.
Meaning: Changes should be evaluated before becoming standard.
“Keep useful telemetry.”
Example: Use this when tuning an alert pipeline.
Meaning: Noise reduction should not eliminate valuable evidence.
“Track recurring benign patterns.”
Example: Use this when the same legitimate behavior appears frequently.
Meaning: Repeated patterns can inform better detection logic.
“Review exclusions carefully.”
Example: Use this when creating exceptions for trusted activity.
Meaning: Exceptions can create blind spots if applied too broadly.
“Measure alert quality.”
Example: Use this during regular SOC performance reviews.
Meaning: Detection quality should be monitored rather than assumed.
“Retest after environmental changes.”
Example: Use this after a major infrastructure migration.
Meaning: Changes can alter detection behavior.
“Document why a rule changed.”
Example: Use this when modifying detection logic.
Meaning: Future analysts need to understand the reasoning behind tuning.
False Positive First Response Best Practices
“Start with verification.”
Example: Use this as the first rule in an analyst checklist.
Meaning: Confirm the alert before treating it as a confirmed incident.
“Keep triage structured.”
Example: Use this when multiple analysts handle the same queue.
Meaning: Consistency makes alert handling easier to manage.
“Use multiple evidence sources.”
Example: Use this when one telemetry source is inconclusive.
Meaning: Correlation can improve confidence.
“Document every meaningful decision.”
Example: Use this when an alert is escalated or closed.
Meaning: Important decisions should be traceable.
“Know the environment.”
Example: Use this when investigating legitimate administrative behavior.
Meaning: Environmental knowledge helps distinguish normal from unusual activity.
“Understand critical assets.”
Example: Use this when prioritizing alerts.
Meaning: Asset importance can influence response decisions.
“Keep escalation paths current.”
Example: Use this when maintaining incident response procedures.
Meaning: Outdated contacts can slow a genuine response.
“Review recurring false positives.”
Example: Use this during monthly security operations reviews.
Meaning: Repeated noise can point to systemic detection issues.
“Do not confuse alerts with incidents.”
Example: Use this when teaching incident response fundamentals.
Meaning: An alert is a signal that still requires analysis.
“Preserve important evidence.”
Example: Use this when an alert could later become an incident.
Meaning: Useful information should remain available.
“Learn from closed alerts.”
Example: Use this when reviewing historical cases.
Meaning: False positives can provide valuable detection lessons.
“Improve the process continuously.”
Example: Use this during security program reviews.
Meaning: Triage should evolve as systems, threats, and detection logic change.
NIST’s current incident response guidance places response within broader cybersecurity risk management, while practical incident workflows commonly distinguish false positives from confirmed incidents during analysis and triage.
False Positive First Response Examples
“The alert was triggered by scheduled maintenance.”
Example: Use this when a planned change explains the detection.
Meaning: The activity has a legitimate operational cause.
“The login matched an approved administrative task.”
Example: Use this when privileged activity was authorized.
Meaning: The alert does not necessarily indicate compromise.
“The endpoint activity came from approved software.”
Example: Use this when known software triggered a detection.
Meaning: The detected behavior has a legitimate source.
“The network connection belongs to an approved service.”
Example: Use this when an external connection initially appears suspicious.
Meaning: The destination has been verified as legitimate.
“The detection rule matched normal automation.”
Example: Use this when a scheduled script triggers an alert.
Meaning: Routine automation created the security signal.
“The alert lacked corroborating indicators.”
Example: Use this when investigation finds no supporting evidence.
Meaning: The alert alone does not establish an incident.
“Historical activity matches the current event.”
Example: Use this when an unusual-looking action is actually routine.
Meaning: Previous behavior provides a legitimate baseline.
“The user confirmed the activity was authorized.”
Example: Use this when user verification supports the investigation.
Meaning: Direct context helps explain the alert.
“The detection was caused by a configuration change.”
Example: Use this when a recent system change explains the behavior.
Meaning: Environmental changes can generate false positives.
“The event was closed after validation.”
Example: Use this when documenting a completed false-positive investigation.
Meaning: The alert was reviewed and resolved.
“The alert requires additional investigation.”
Example: Use this when evidence remains inconclusive.
Meaning: The case should not be prematurely dismissed.
“The event was escalated after correlation.”
Example: Use this when additional evidence supports malicious activity.
Meaning: Corroboration changed the initial assessment.
False Positive First Response Checklist
“Verify the alert.”
Example: Use this as the first item on an analyst checklist.
Meaning: Confirm that the underlying event is real.
“Identify the affected asset.”
Example: Use this when beginning an endpoint or network investigation.
Meaning: Establish exactly what is involved.
“Identify the user or account.”
Example: Use this when authentication activity triggers the alert.
Meaning: Identity context can clarify the event.
“Review timestamps.”
Example: Use this when correlating several logs.
Meaning: Timing helps determine whether events belong together.
“Check recent changes.”
Example: Use this when the alert follows maintenance or deployment activity.
Meaning: Recent changes can explain unusual behavior.
“Correlate supporting evidence.”
Example: Use this when the initial alert is incomplete.
Meaning: Multiple signals provide stronger context.
“Check for legitimate explanations.”
Example: Use this when activity could be normal business behavior.
Meaning: Authorized activity should be considered before escalation.
“Assess potential impact.”
Example: Use this when the alert cannot yet be dismissed.
Meaning: Impact helps determine appropriate handling.
“Document the investigation.”
Example: Use this when closing or escalating the case.
Meaning: The investigation should have a clear record.
“Assign the appropriate disposition.”
Example: Use this when completing triage.
Meaning: The alert should be categorized based on available evidence.
“Escalate when justified.”
Example: Use this when supporting evidence indicates a genuine threat.
Meaning: Credible risk should move through the incident response process.
“Review what can be improved.”
Example: Use this after repeated false positives.
Meaning: Every investigation can reveal opportunities to improve detection and response.
FAQs
What does false positive first response mean?
It refers to the initial process of validating a security alert to determine whether it represents a genuine security issue or benign activity before further escalation.
Why is false positive first response important?
It helps analysts avoid wasting response resources on harmless events while still giving potentially genuine incidents appropriate attention.
What is the first thing to do with a suspected false positive?
Start by verifying the alert and reviewing its supporting context. Check relevant logs, affected assets, user activity, and other indicators before deciding how to proceed.
Should a false positive be ignored?
No. It should be investigated enough to establish why the alert was generated and then documented with an appropriate disposition.
What is the difference between an alert and an incident?
An alert is a signal generated by a security control or monitoring system. An incident requires further analysis and classification before it is treated as a confirmed security event.
Can false positives cause security problems?
Yes. Excessive false positives can consume analyst time and make meaningful alerts harder to prioritize. Poor-quality detections can also slow response by adding unnecessary investigation workload.
Should false positives be documented?
Yes. Documentation helps explain why an alert was closed and can reveal recurring patterns that may benefit from detection tuning.
When should a false positive be escalated?
Escalation may be appropriate when the evidence remains uncertain, the potential impact is significant, or additional indicators suggest genuine malicious activity.
Can automation handle false positives?
Automation can assist with filtering, enrichment, correlation, and other repetitive tasks, but high-impact decisions may still require appropriate human oversight.
What evidence should analysts check first?
Useful evidence can include the original alert, timestamps, affected assets, users, logs, recent changes, network activity, endpoint activity, and related detections.
How can organizations reduce false positives?
Organizations can improve detection logic, review recurring benign patterns, tune thresholds carefully, maintain accurate asset context, and regularly evaluate detection performance.
What should happen after a false positive is confirmed?
Each alert should have a documented disposition, relevant evidence should be retained, and recurring issues should inform detection and workflow improvements.
Conclusion
A good false positive first response is less about panic and more about disciplined curiosity. When an alert appears, the goal is not to immediately declare victory or disaster. Start by verifying the signal, checking context, correlating evidence, documenting what you discover, and escalating when the facts justify it.
That approach can make security operations calmer, clearer, and easier to scale. It also turns false positives into useful learning opportunities because recurring benign alerts can reveal where detection rules or workflows need attention. Whether you work in a SOC, IT team, or incident response function, keep the process practical and consistent. Save this guide, share it with your security team, and use the checklist whenever an alert says, “Hey, look at me.”